---
updatedAt: 2025-10-31T07:22:45.000Z
agentTools:
projectIndex: https://help.zluri.com/llms.txt
---
# Okta SAML
Log in to Zluri through Okta
To enable clients to log in to Zluri through Okta, you'll need to set up SAML.
**Important:** As of now, Zluri supports SAML **only** through a **custom app integration** in Okta.
Zluri’s SAML setup **cannot** be completed using the Zluri application listed in the Okta catalog. The catalog app does **not** allow adding Zluri’s ACS URL and Audience URI, which are required for configuration.
Always create a **custom SAML 2.0 app integration** instead.
If your organization has been anonymized and recreated using the same name, contact Zluri Support before reconfiguring SAML.\
Old SAML connections tied to the same organization name may need cleanup in Auth0 to avoid setup conflicts.
## Configuration steps
### Select domains allowed for SSO in Zluri
In Zluri, navigate to [Settings → SSO](https://app.zluri.com/settings/sso) and select the domains allowed for SSO login. Click **Save** when done.
If your domain is not listed, you can add it from [Settings → Directory Management](https://app.zluri.com/settings/directory-management).
### Configure SAML in Okta
1. Go to your Okta Admin Console.
2. In the Admin Console, go to **Applications** → **Applications**.
3. Click **Create App Integration**.
4. Select **SAML 2.0**.
5. Click **Next**.
6. In **General settings**, enter an app name, e.g., Zluri SAML.
7. Click **Next**.
8. In **SAML Settings**, configure the following:
1. Single sign-on URL and audience URI from [SSO Settings](https://app.zluri.com/settings/sso)
* Single sign-on URL = ACS URL
* Audience URI = SP Entity ID)
9. Attribute Statements:
1. **Name**: email
2. **Name format**: unspecified
3. **Value**: user.email\
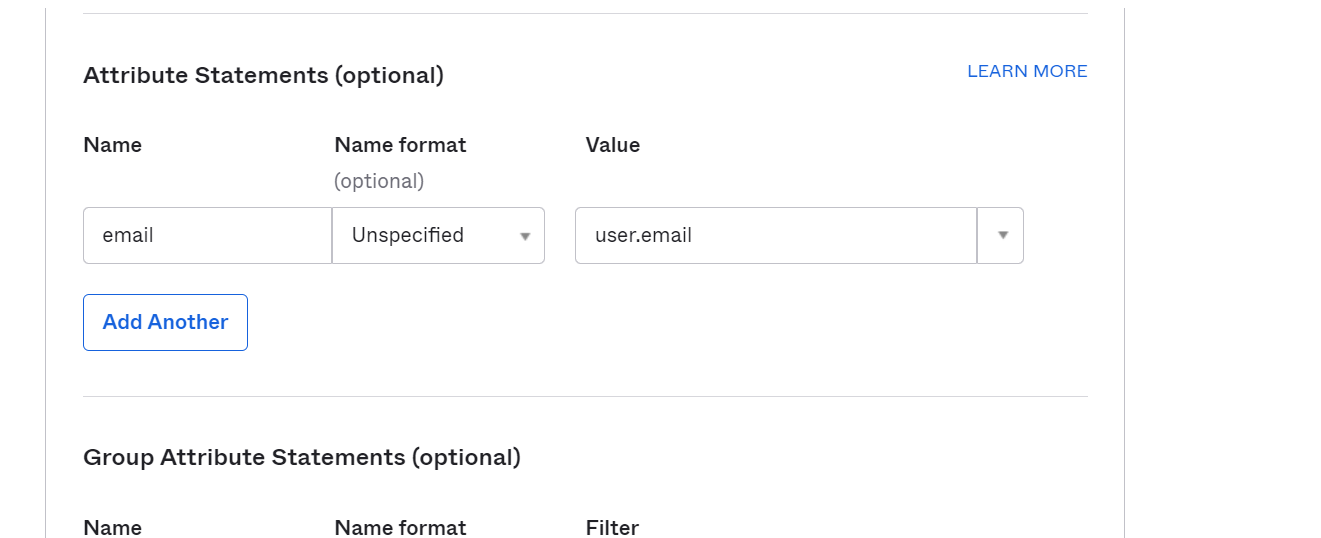
10. Click **Next**.
11. Select **I'm an Okta customer adding an internal app** and **This is an internal app that we have created**.
12. Click **Finish**.
13. In the **Settings** section of the Sign On tab, locate and click on **View SAML setup instructions** on the right side and copy the Identity Provider Single Sign-On URL:
14. Download the certificate required to upload on the Zluri dashboard.
15. Assign the app to all the users by clicking on assign to groups.
### Configure sign in URL and signing certificate in Zluri
In Zluri's [SSO Settings](https://app.zluri.com/settings/sso), enter the sign-in URL you obtained in step 13, upload the certificate you downloaded in step 14, then click **Save**.
Finally, click **Test connection** to try logging in with your Okta credentials. If you can log in successfully, then it works. Next time any user of your organization tries to log in they will be redirected to the Okta login page.
## Editing an existing SAML setup
### Rotate SAML certificates
X.509 certificates have a defined lifetime (e.g., in Google Workspace, it has a validity of 5 years). You should rotate a certificate if it's about to expire or if it becomes compromised.
If a certificate expires before you rotate it, your users won’t be able to use SSO to sign in to any SAML applications that use that certificate until you replace it with a new certificate.
To rotate the certificate:
1. Open the SAML app in your SSO, navigate to the certificate page, and recreate it.
2. Once you get the new certificate, please upload it to the Zluri platform.
Save the connection, and you can continue to use the SAML connection as configured.
### Add/remove SAML domains
To add or remove SAML domains, go to [SSO Settings](https://app.zluri.com/settings/sso), select/deselect the domains that you want to configure for SAML, then click **Save**.
### Need help?
If you face issues during setup, ensure that:
* The app created in Okta is **active**.
* User attributes (like `user.email`) are correctly mapped.
* The **Sign-on URL** in Zluri matches the one from your **custom app**, not the catalog app.
If problems persist, Feel free to [submit a ticket](https://support.zluri.com/support/tickets/new) or contact us directly at .