---
updatedAt: 2026-03-30T08:17:36.000Z
agentTools:
projectIndex: https://help.zluri.com/llms.txt
---
# Connect Via SSO
Connect Jamf Pro to Zluri via SSO
## Prerequisites
* **Administrator** privileges in Jamf Pro (to create API role and client)
* **SSO Enabled**:
* **Enabled**: If SSO is enabled, you need to generate Client ID, Client Secrets and Organisation Subdomain.
* **Disabled**: If SSO is disabled, you can connect with Username, Password and Organisation Subdomain.
**Username** and **Password** should be of an **administrator** in Jamf Pro.
## Integration steps
### Create an API role
1. [Log in](https://account.jamf.com/login) to Jamf Pro.
2. Click **Settings** in the sidebar.
3. In the **System** section, click **API Roles and Clients**.
4. Click the **API Roles** tab at the top of the pane.
5. Click **New**.
6. Enter a display name for the API role.
7. In the Jamf Pro API role privileges field, search for and assign the following privileges:
1. Read User Extension Attributes
2. Read Static User Groups
3. Read Smart User Groups
4. Read User
5. View JSS Information
6. Read Advanced Computer Searches
7. Read Computers
8. Click **Save**.
### Create an API Client
1. In Jamf Pro, click **Settings** in the sidebar.
2. In the **System** section, click **API roles and clients**.
3. Click the **APl Clients** tab at the top of the pane.
4. Click **New**.
5. Enter a display name for the API client, e.g., `zluri-integration`.
6. In the **API Roles** field, assign the previously created role.
7. Under **Access Token Lifetime**, enter the time in seconds that you want access tokens to be valid for.
8. Click **Save**.
9. Click **Edit**.
10. Click **Enable API Client**.
11. Click **Save**.
### Generate a client secret
1. Navigate to the API client created above and click **Generate Client Secret**.
2. Click **Create Secret** in the confirmation dialog.
3. Copy and save the client secret in a secure location.
### Connect the Jamf Pro instance in Zluri
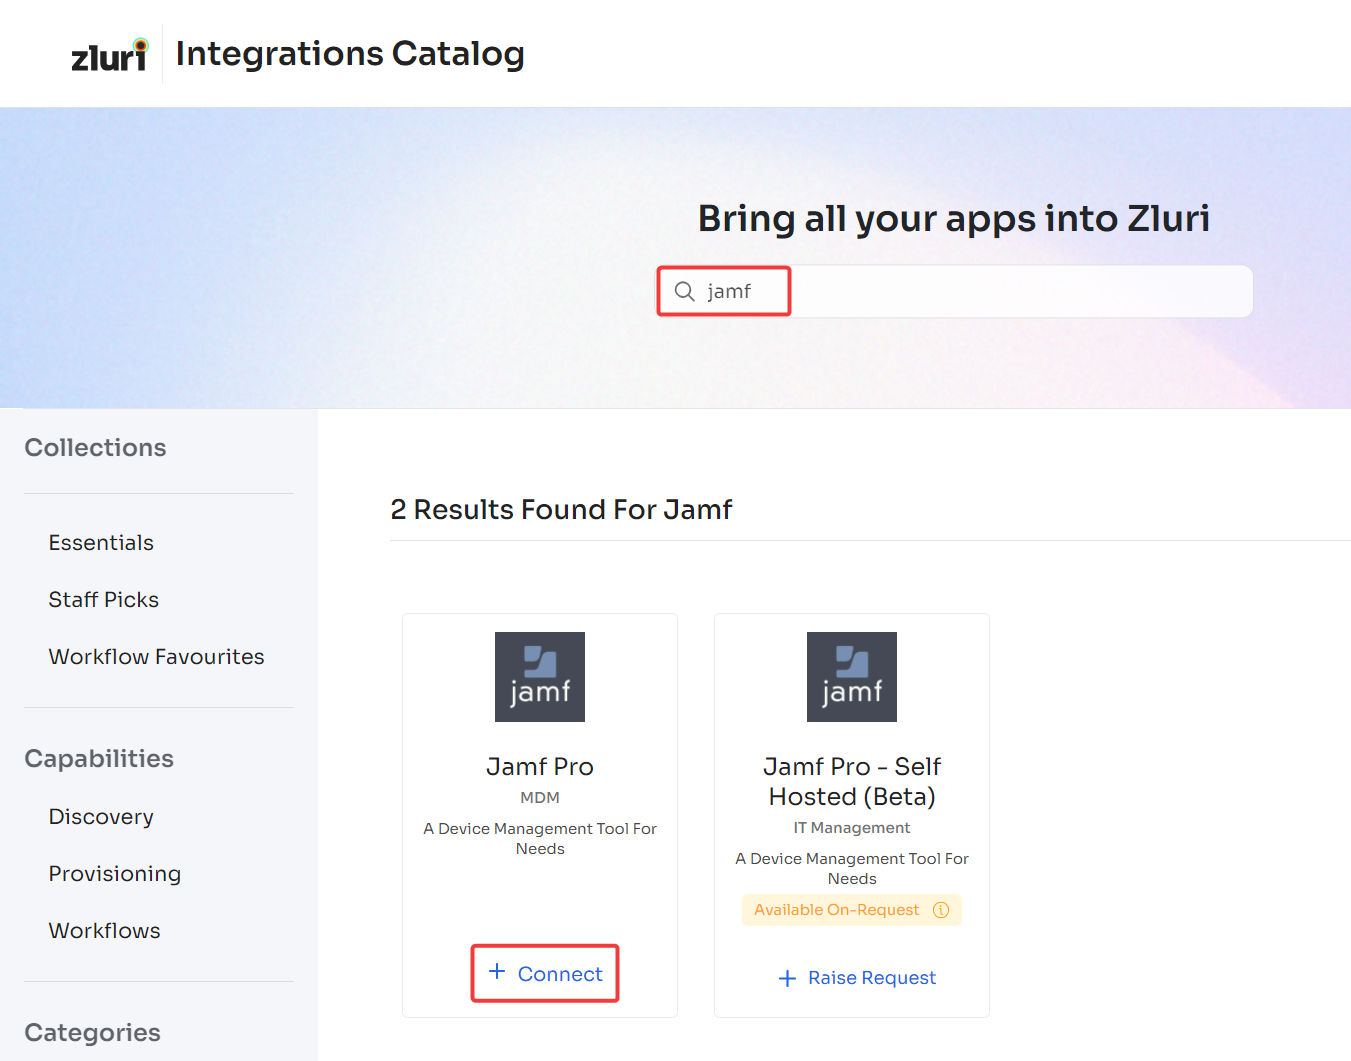
1. Open the [Integrations Catalog](https://app.zluri.com/integrations/catalog), search for “jamf pro”, and click ➕ **Connect**.
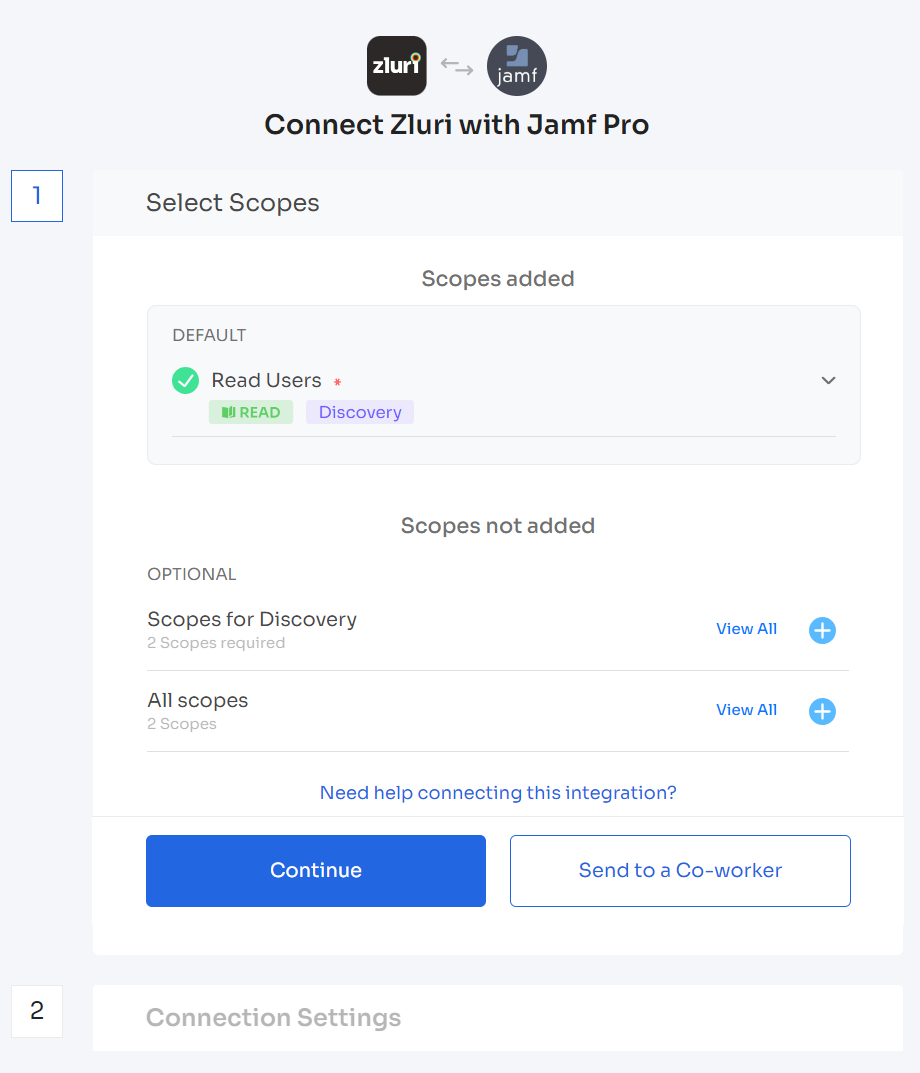
2. Choose the scopes for the integration, and click **Continue**. You can click the down-arrow button towards the right of a scope to find out what it does.
If you added the [optional privileges](#optional-privileges) while creating the API role, select the optional scopes here as well.
3. Fill out the fields as follows:
1. **Username / Client ID**: Enter the client ID created above
2. **Password / Client secret**: Enter the secret for the client ID
3. **Organization Subdomain**: Your company's Jamf Pro subdomain, for example, if you access Jamf through `umbrellacorp.jamfcloud.com`, enter `umbrellacorp` here.
4. **SSO**: Set to **Enabled**
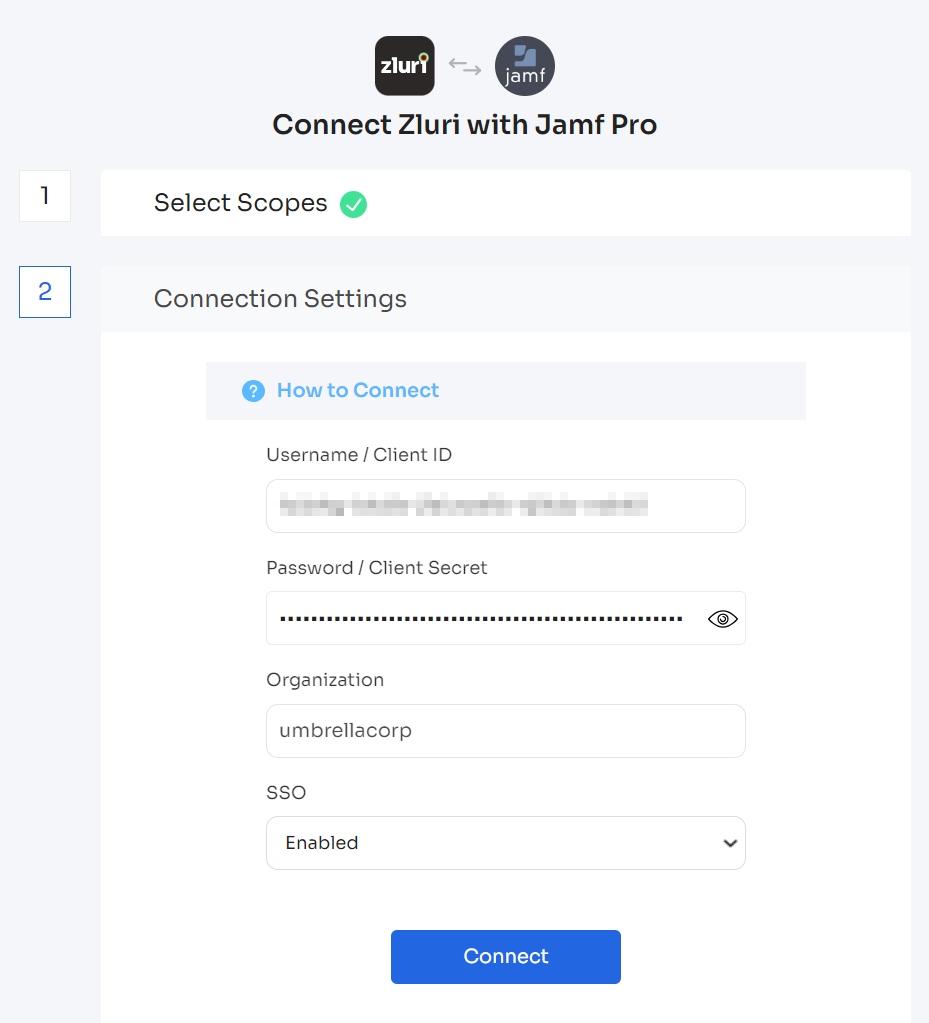
4. Click **Connect**, give the connection a name and description, and you’re ready to go!
Got questions? Feel free to [submit a ticket](https://support.zluri.com/support/tickets/new) or contact us directly at .