---
updatedAt: 2026-07-29T10:07:40.000Z
agentTools:
projectIndex: https://help.zluri.com/llms.txt
---
# Connect
Connect Microsoft Active Directory to Zluri
## Prerequisites
* **Administrator** privileges on the Active Directory server
## Locate the Active Directory integration and choose scopes
1. Open the [Integrations Catalog](https://app.zluri.com/integrations/catalog), search for "active directory", and click ➕ **Connect**.
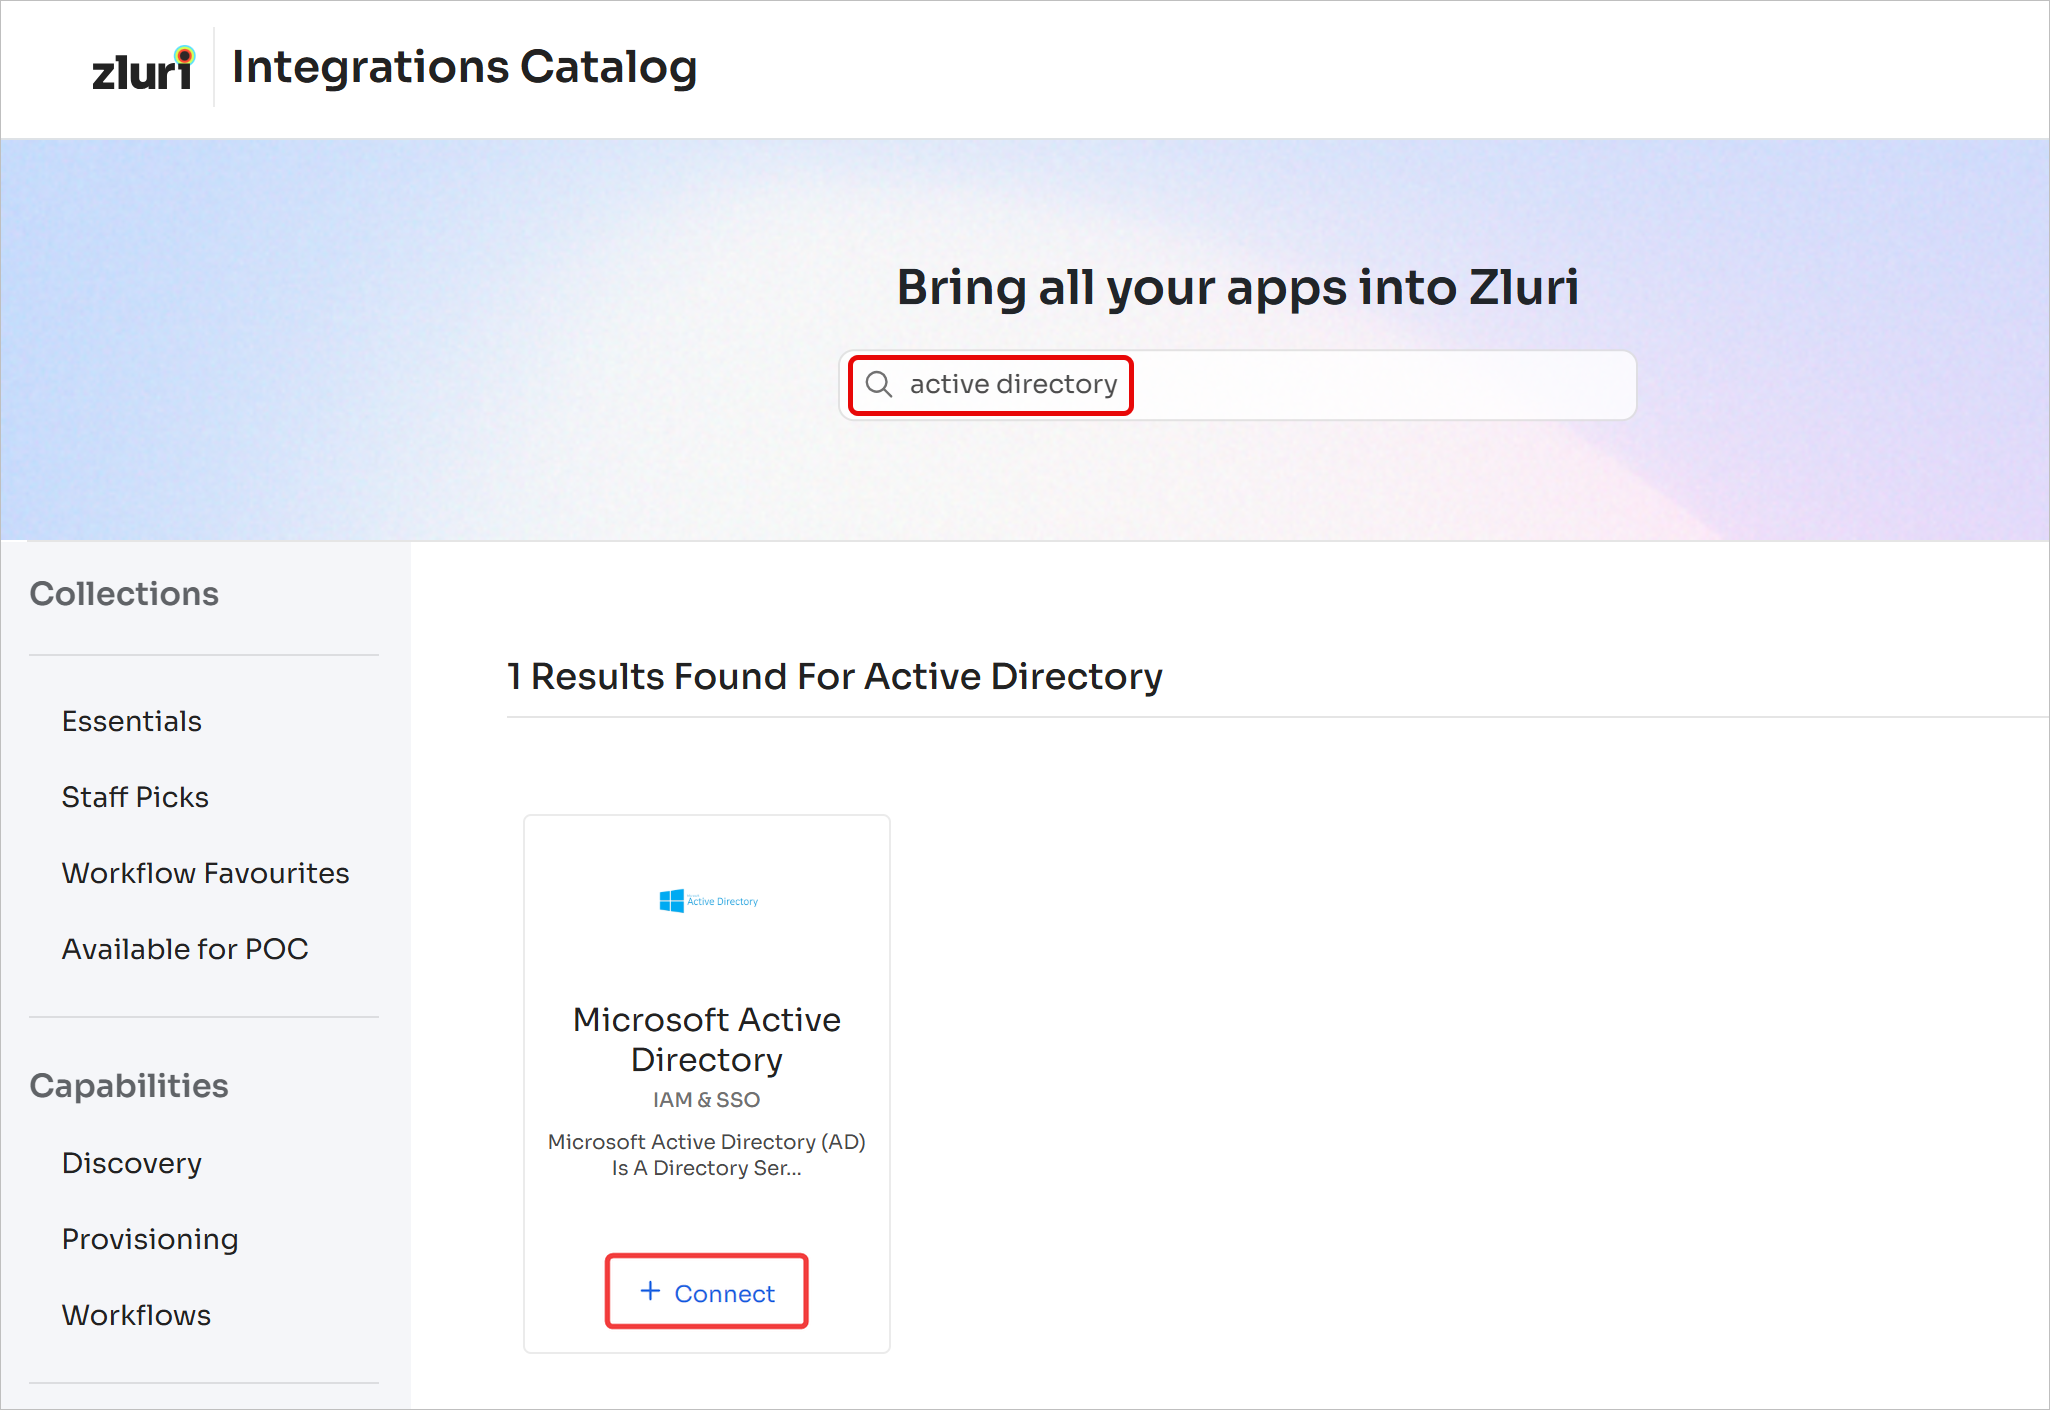
2. Choose the scopes for the integration, and click **Continue**. You can click the down-arrow button towards the right of a scope to find out what it does.
## Gather information about your server
Fill out your server information. You'll find the steps to gather this information below this screenshot.
### a. On Prem Server Host
This is your server's external IP address. To find this, open `cmd.exe` and run `curl ifconfig.me/ip`
### b. On Prem Server Port
If you have [SSL enabled](#c-ssl-enabled-on-on-prem-server) on your domain controller, enter **636**. Otherwise, enter **389**
### c. SSL Enabled On On Prem Server
Check if the domain controller has an active SSL certificate:
1. Press **Windows** + **R**, and run `mmc.exe`
2. Go to **File** → **Add/Remove Snap-in...**
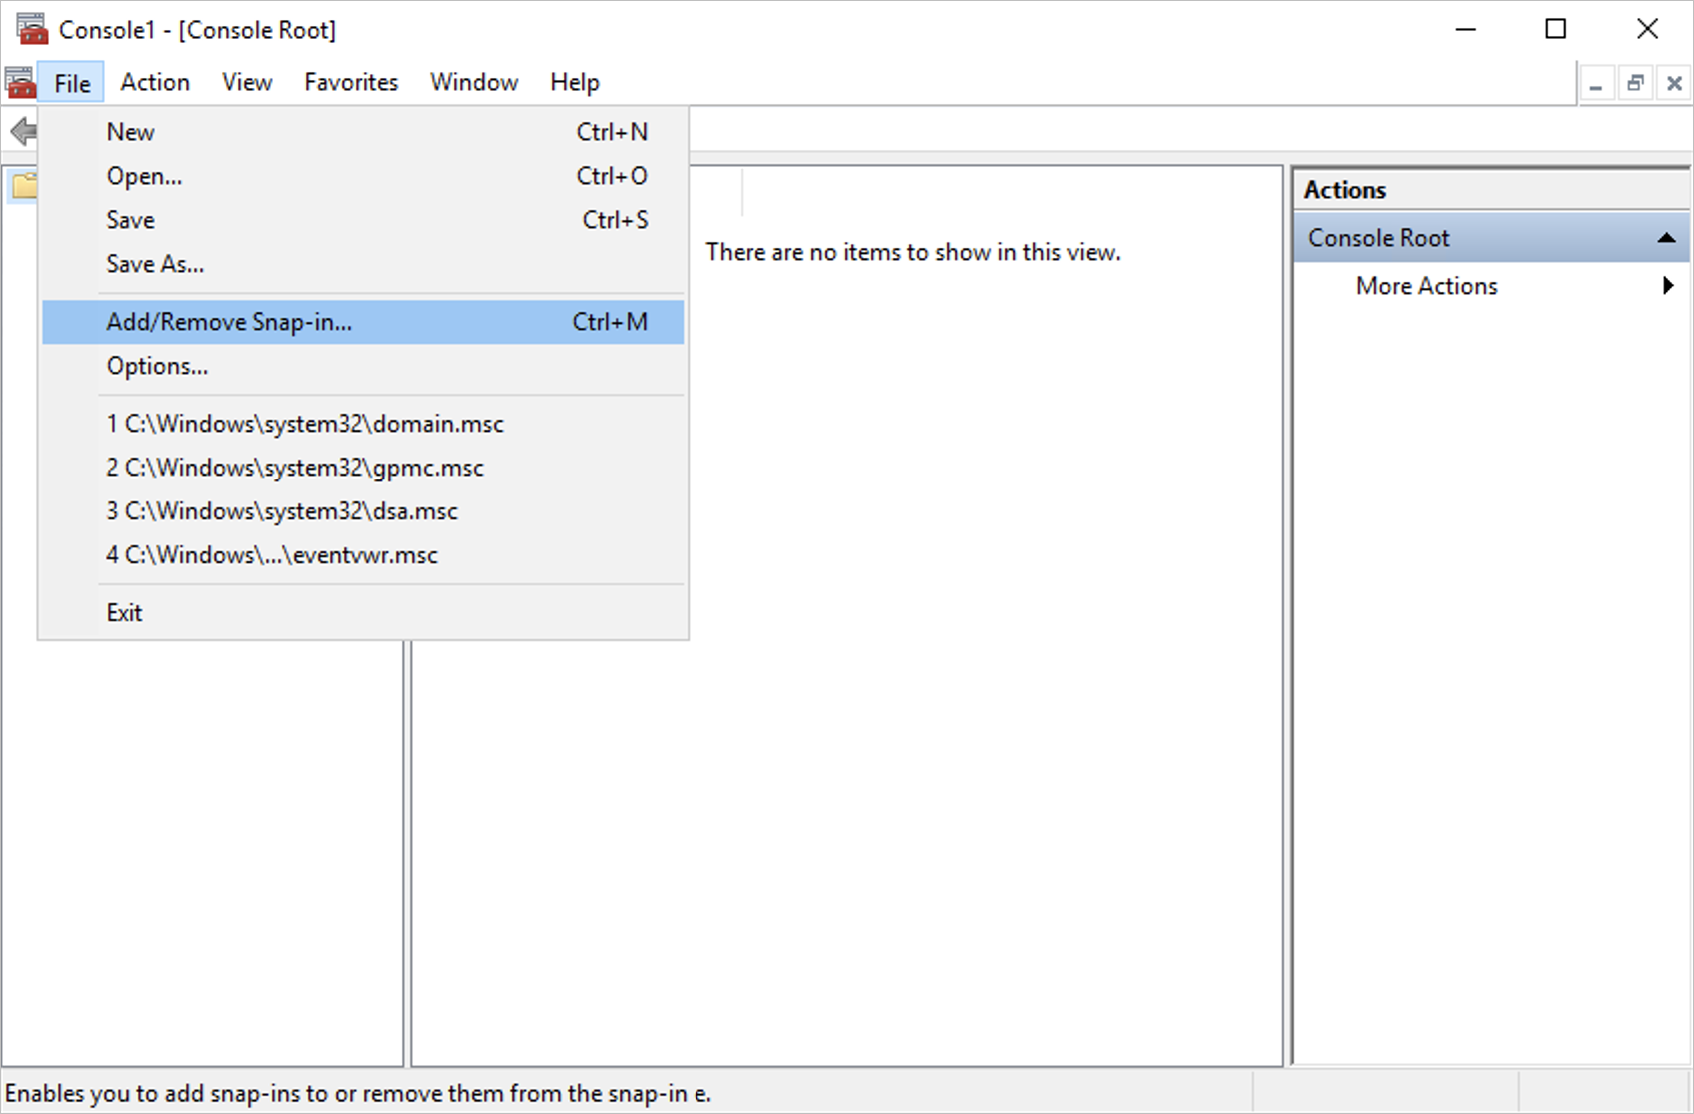
3. Select **Certificates** from the list and click **Add**
4. Choose **Computer account** and click **Next**
5. Select **Local computer** and click **Finish**
6. Click **OK** to close the snap-in window
7. In the left pane, expand: **Certificates (Local Computer)** → **Personal** → **Certificates**
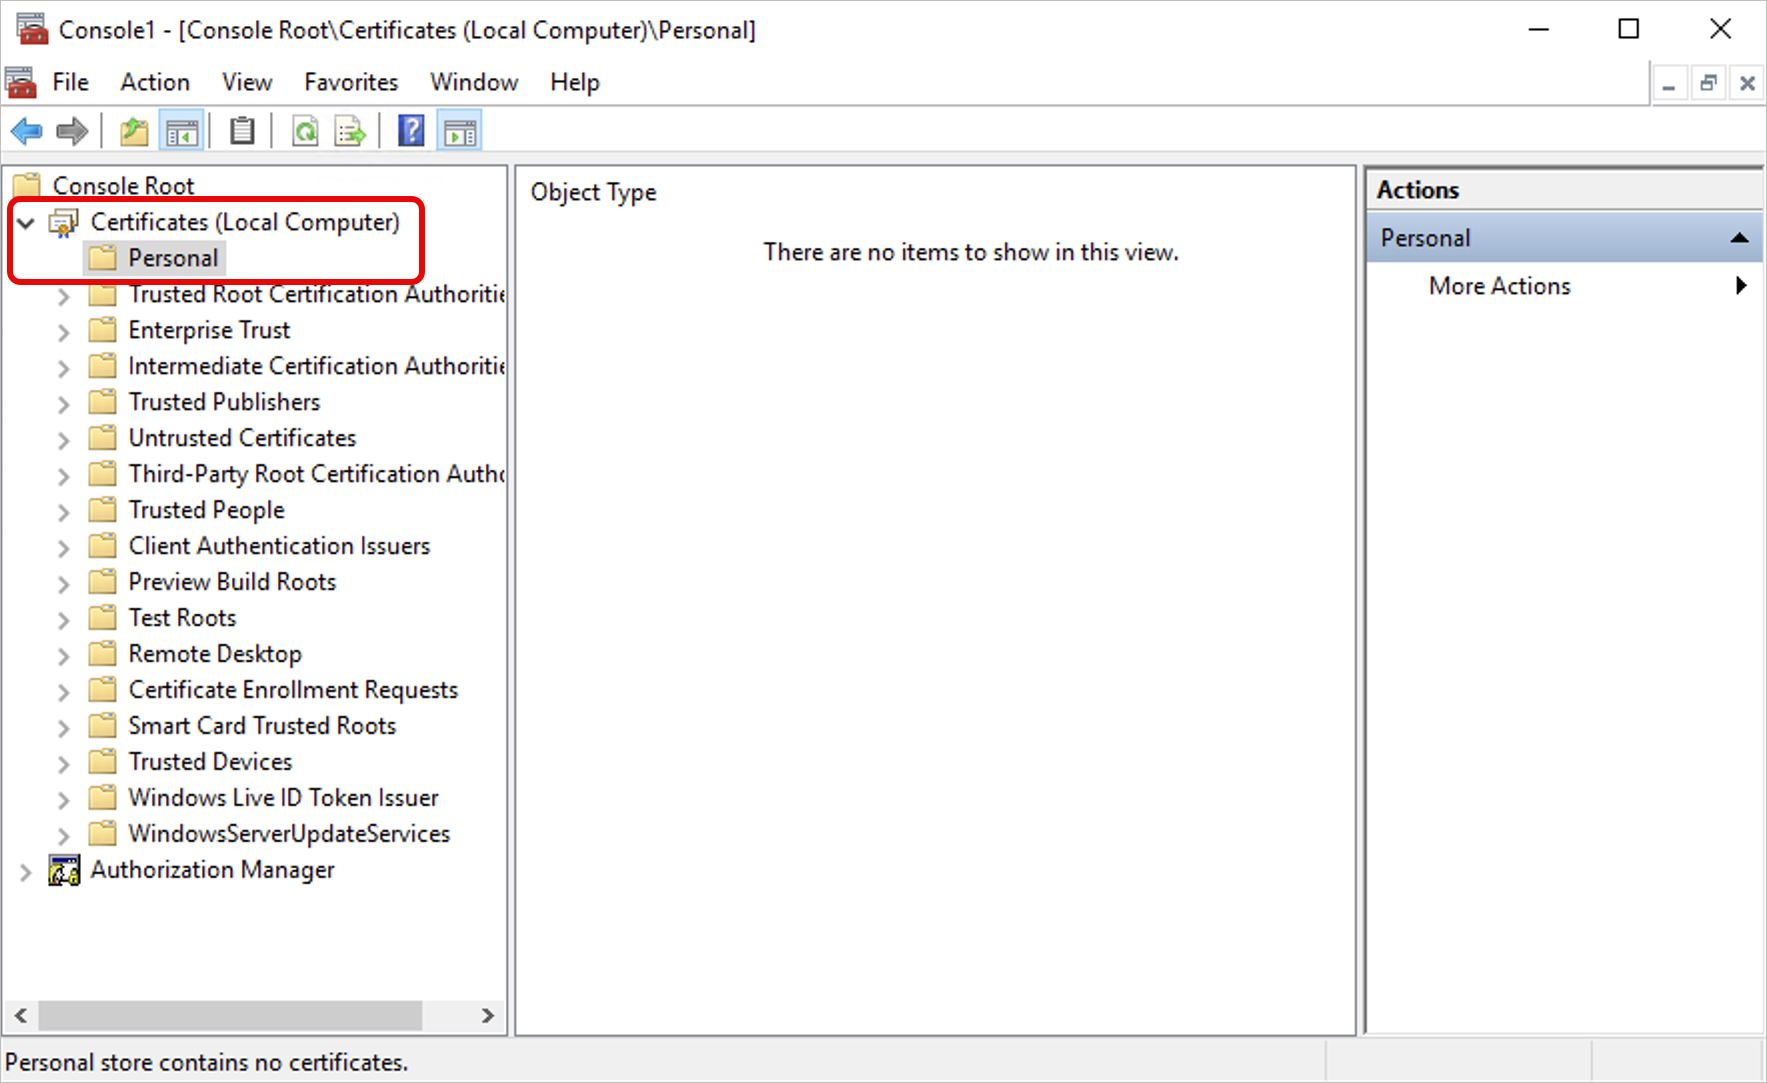
8. Look for a certificate with:
1. **Subject**: The DC’s hostname
2. **Purpose**: Server Authentication
In this case, there is no such certificate, so we will choose **No**. If the certificate exists, set the field to **Yes** instead.
### d. Base DN of On Prem Server
Distinguished Name (DN) for the root of your AD domain, (e.g., `dc=acme,dc=com`) . To find this, open **PowerShell** and run the following command:
```powershell
(Get-ADDomain).DistinguishedName
```
### e. Admin Bind DN
Distinguished name of the account binding to LDAP, eg., `cn=Administrator,cn=Users,dc=acme,dc=com` . To find this, open **PowerShell** and run the following command:
```powershell
(Get-ADUser -Identity "Administrator").DistinguishedName
```
### f. Password for On Prem Server
Password of the account used in the previous step.
## Connect the Active Directory instance to Zluri
Click **Connect**, give the connection a name and description, and you’re ready to go!
Got questions? Feel free to [submit a ticket](https://support.zluri.com/support/tickets/new) or contact us directly at .