Performing Access Reviews
For Reviewers (via Employee View) and Certification Owners
1. Introduction
Zluri enables designated reviewers such as application owners, department heads, reporting managers, or individual users to participate in access certifications through the Employee View.
Reviewers are responsible for:
- Logging in using organization-provided SSO (Google or SAML) Learn more about configuring SAML here.
- Accessing assigned certifications
- Reviewing access for records within specific applications or groups
- Selecting appropriate review actions: approve, revoke, or modify
- Providing justification comments where required (mandatory for revoke or modify)
- Confirming their actions by signing off once all assigned records are reviewed
Zluri applies self-review configurations to ensure objectivity:
- If Allow Self Review is enabled, reviewers may act on their own access records.
- If Auto-Reassign is enabled, such records are reassigned automatically to a different role or user (e.g., Reporting Manager, Department Head, Certification Owner, Fallback Reviewer).
Once all reviews are completed and signed off:
- If the certification is single-level, it proceeds to remediation, where admins or certification owners validate the outcomes and trigger playbooks.
- If the certification is multi-level, the records progress to the next level of reviewers, who continue the review cycle before remediation begins.
2. Accessing Assigned Certifications
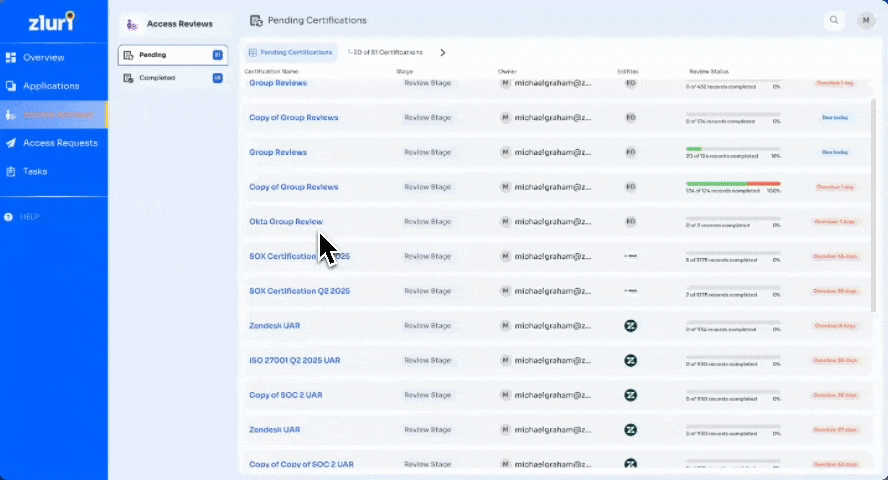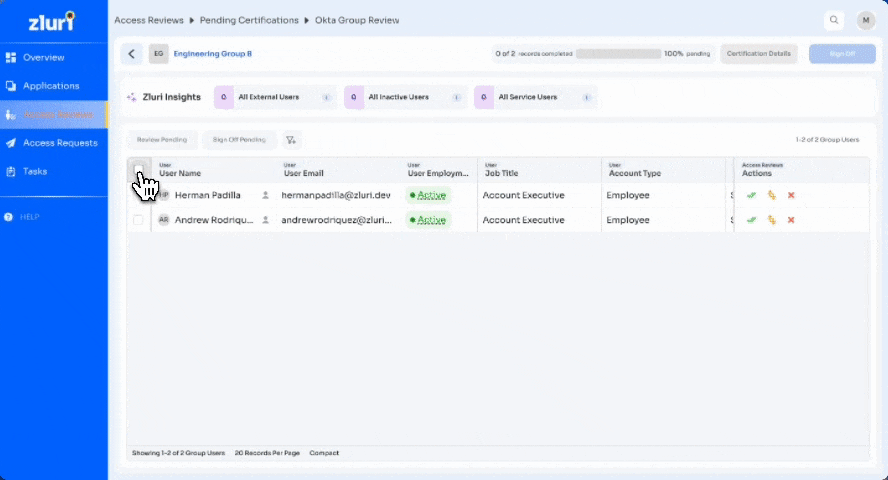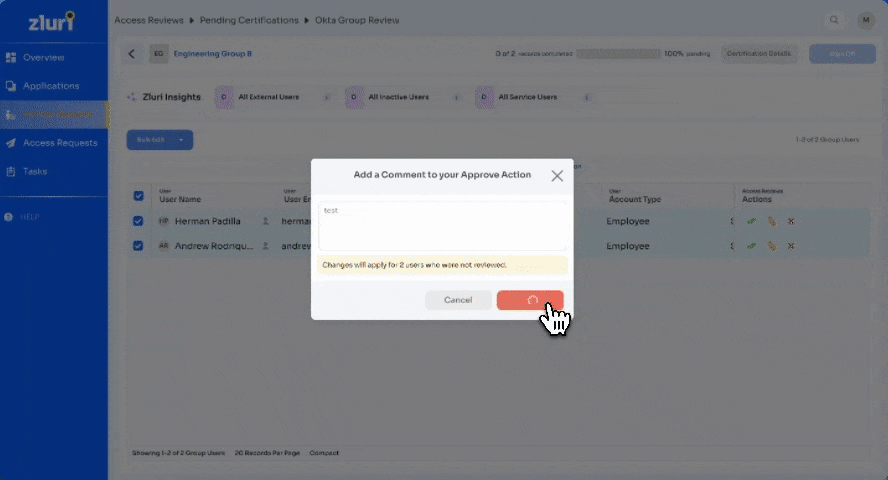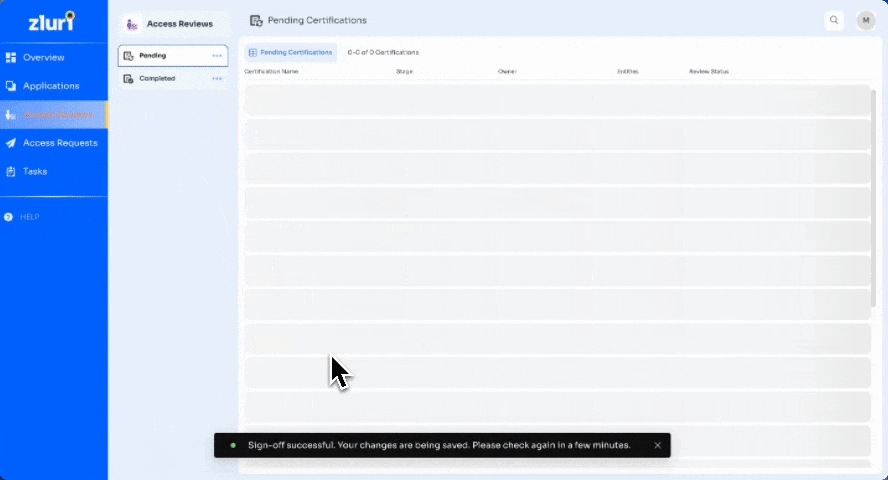
Reviewers can access all assigned access certifications from the Access Reviews tab in the Employee View.
Steps:
- Log in to the Zluri Employee View.
- Select on Access Reviews from the left sidebar.
- Two tabs are available:
- Pending Reviews – Shows all ongoing certifications and entities where the reviewer still has records to review and sign off.
- Completed – Shows all ongoing or completed certifications where the reviewer has finished reviewing and signed off on all records assigned to them.
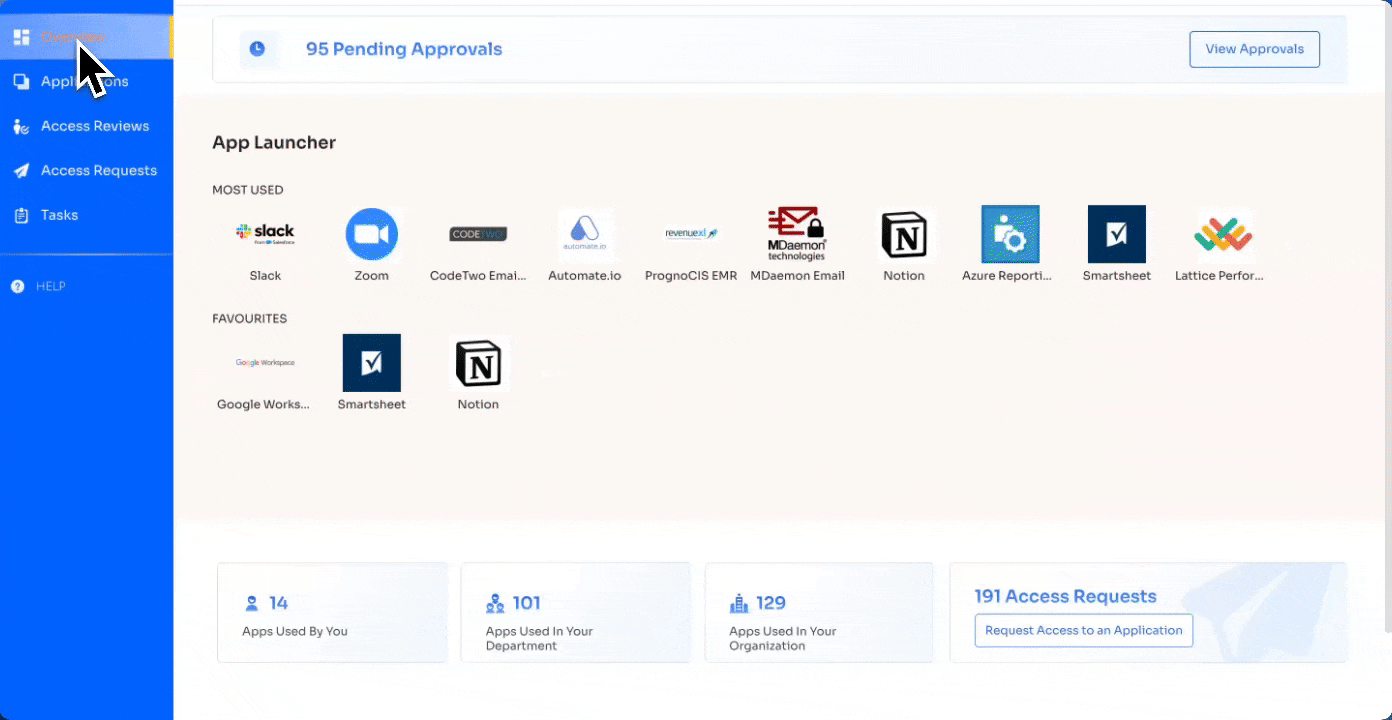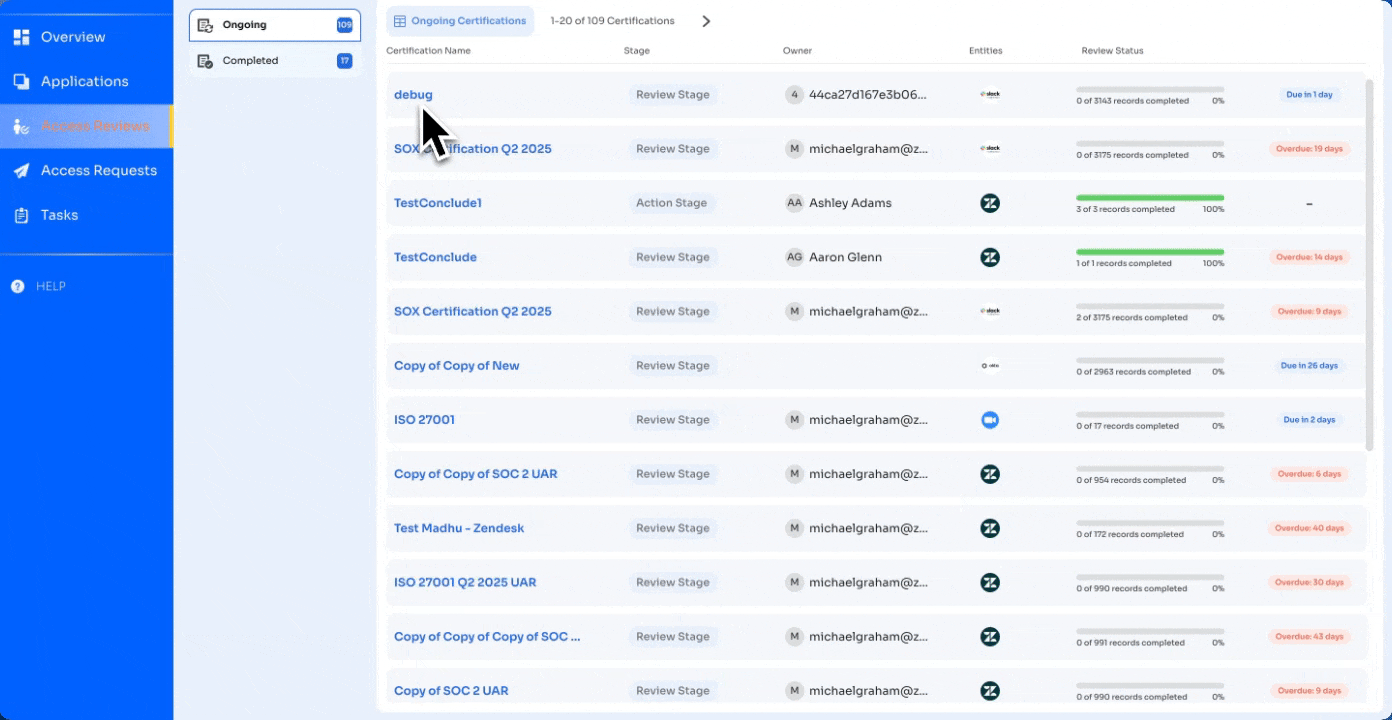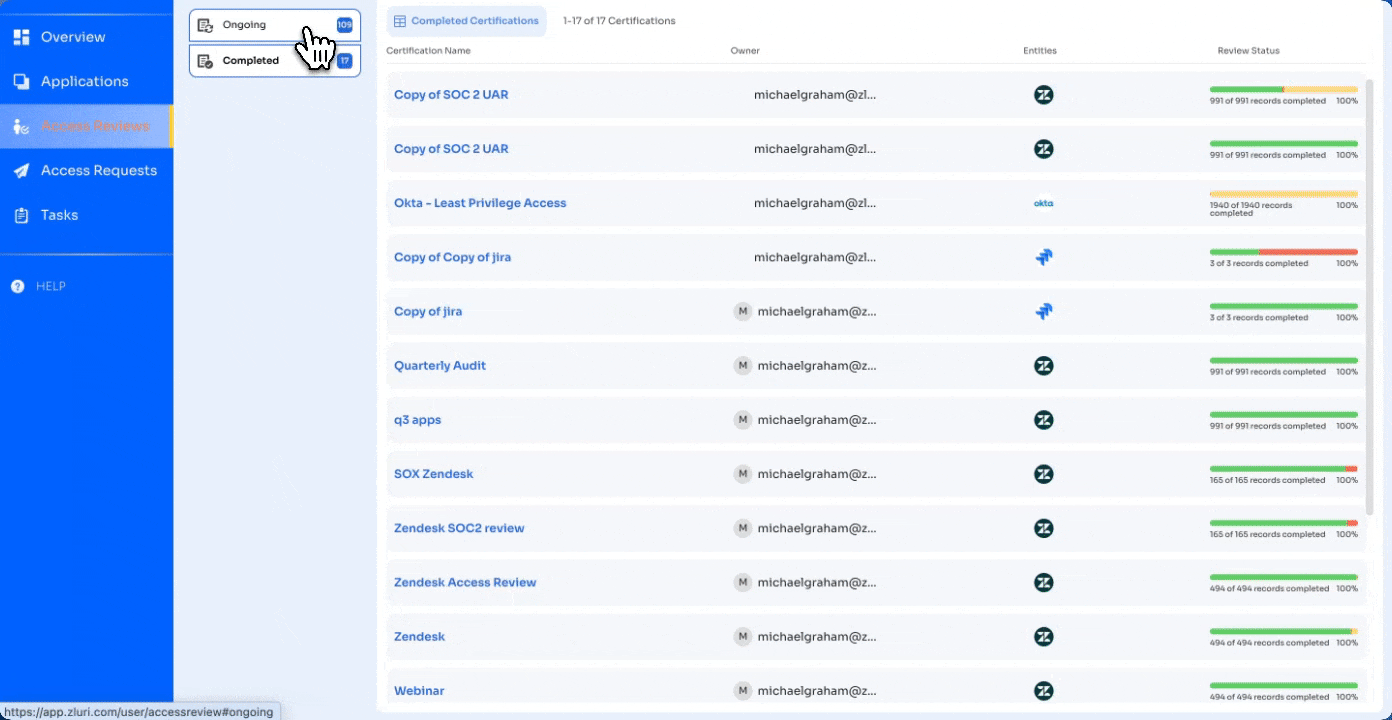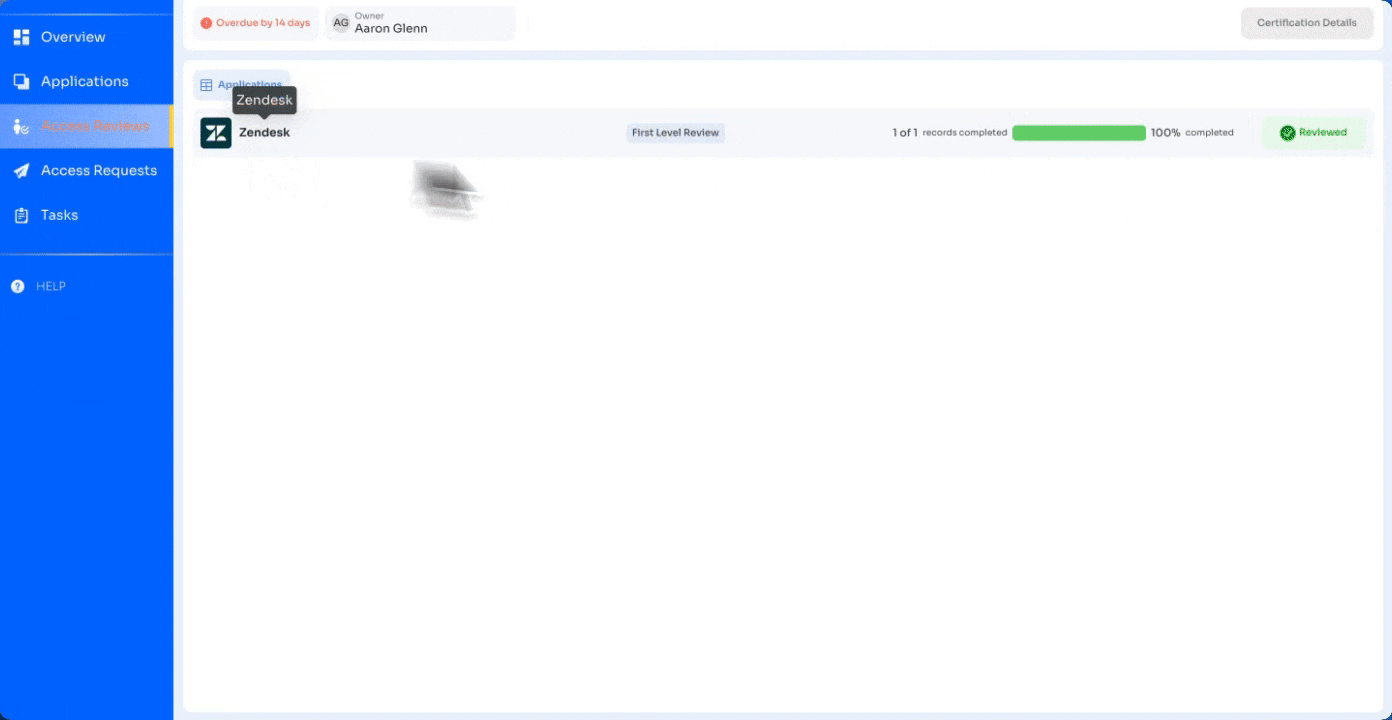
- Under Ongoing Certifications, each row includes:
- Certification Name
- Stage (e.g., Review Stage, Action Stage)
- Certification Owner
- Entities (e.g., app logos; for group reviews, group metadata like group name, number of members, and group source will be displayed)
- Review Status (Shows the number of records signed off and the number reviewed, against the total. The signed off count appears first, in blue. The reviewed count appears beside it in grey.)
- Progress bar – Sits under the counts and separates the two. Hovering over the bar opens a breakdown showing Total Records, Reviewed and Signed Off, Reviewed, Sign Off Pending, and Review Pending.
- Due Date with status indicators (e.g., “Overdue: 5 days” or “Due in 6 days”)
-
To begin a review, select any certification listed under the Ongoing tab.
-
Once selected, the interface will show all assigned applications or groups for that certification.
Opening a certification shows the same counts in two places. The page header carries the counts for the whole certification, and the Review Status column carries them for each application or group inside it.
What’s Editable vs Locked
- Editable:
- While the certification is in the Ongoing tab, the assigned Current Reviewer can edit their decisions for each record (approve, modify, or revoke).
- Comments can be added or updated (for Revoke or Modify actions) until the reviewer signs off.
- Locked:
- After the reviewer selects Sign Off, the actions become locked and no further edits can be made to the decisions or comments for that record.
- Once the Sign Off is complete, the records are locked for that reviewer, and the process moves to the next stage of the review lifecycle.
Application vs Group Reviews UI
-
Application Reviews:
-
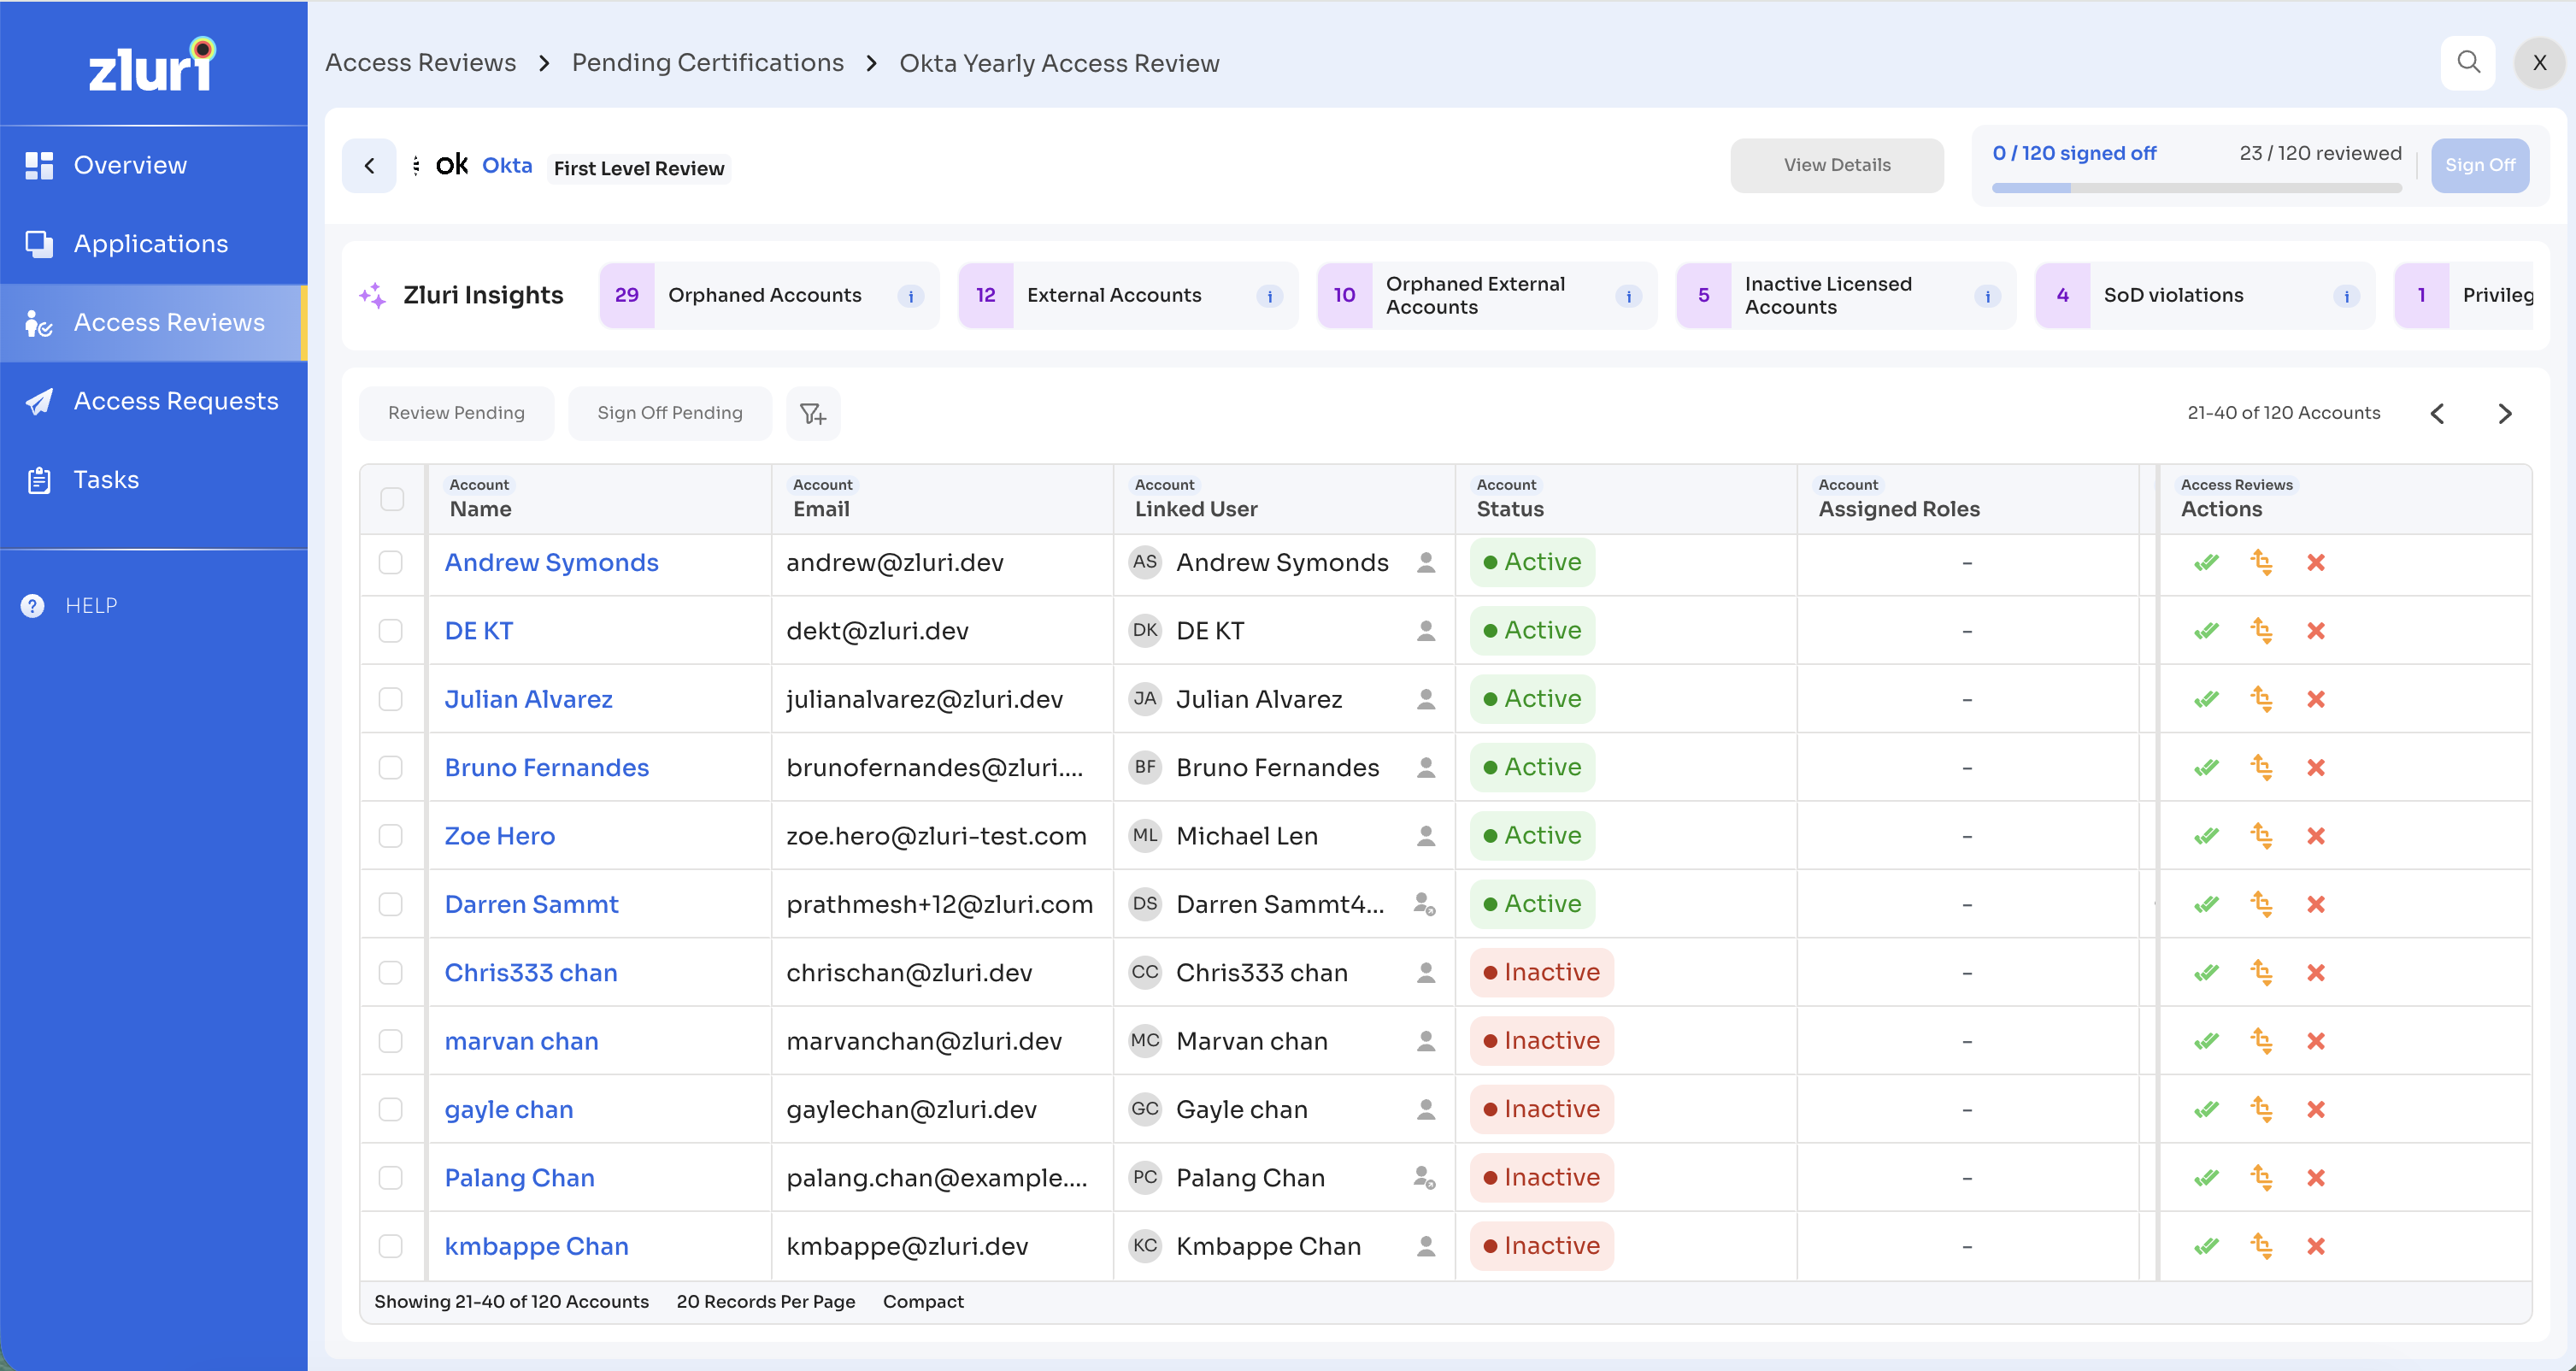
The UI for reviewing applications displays records tied to specific apps.
-
The visible attributes (e.g., access status, assigned licenses, roles, last login) depend on what the certification creator chose while setting up the certification.
-
Reviewers can take actions based on these user attributes.
-
-
Group Reviews:
-
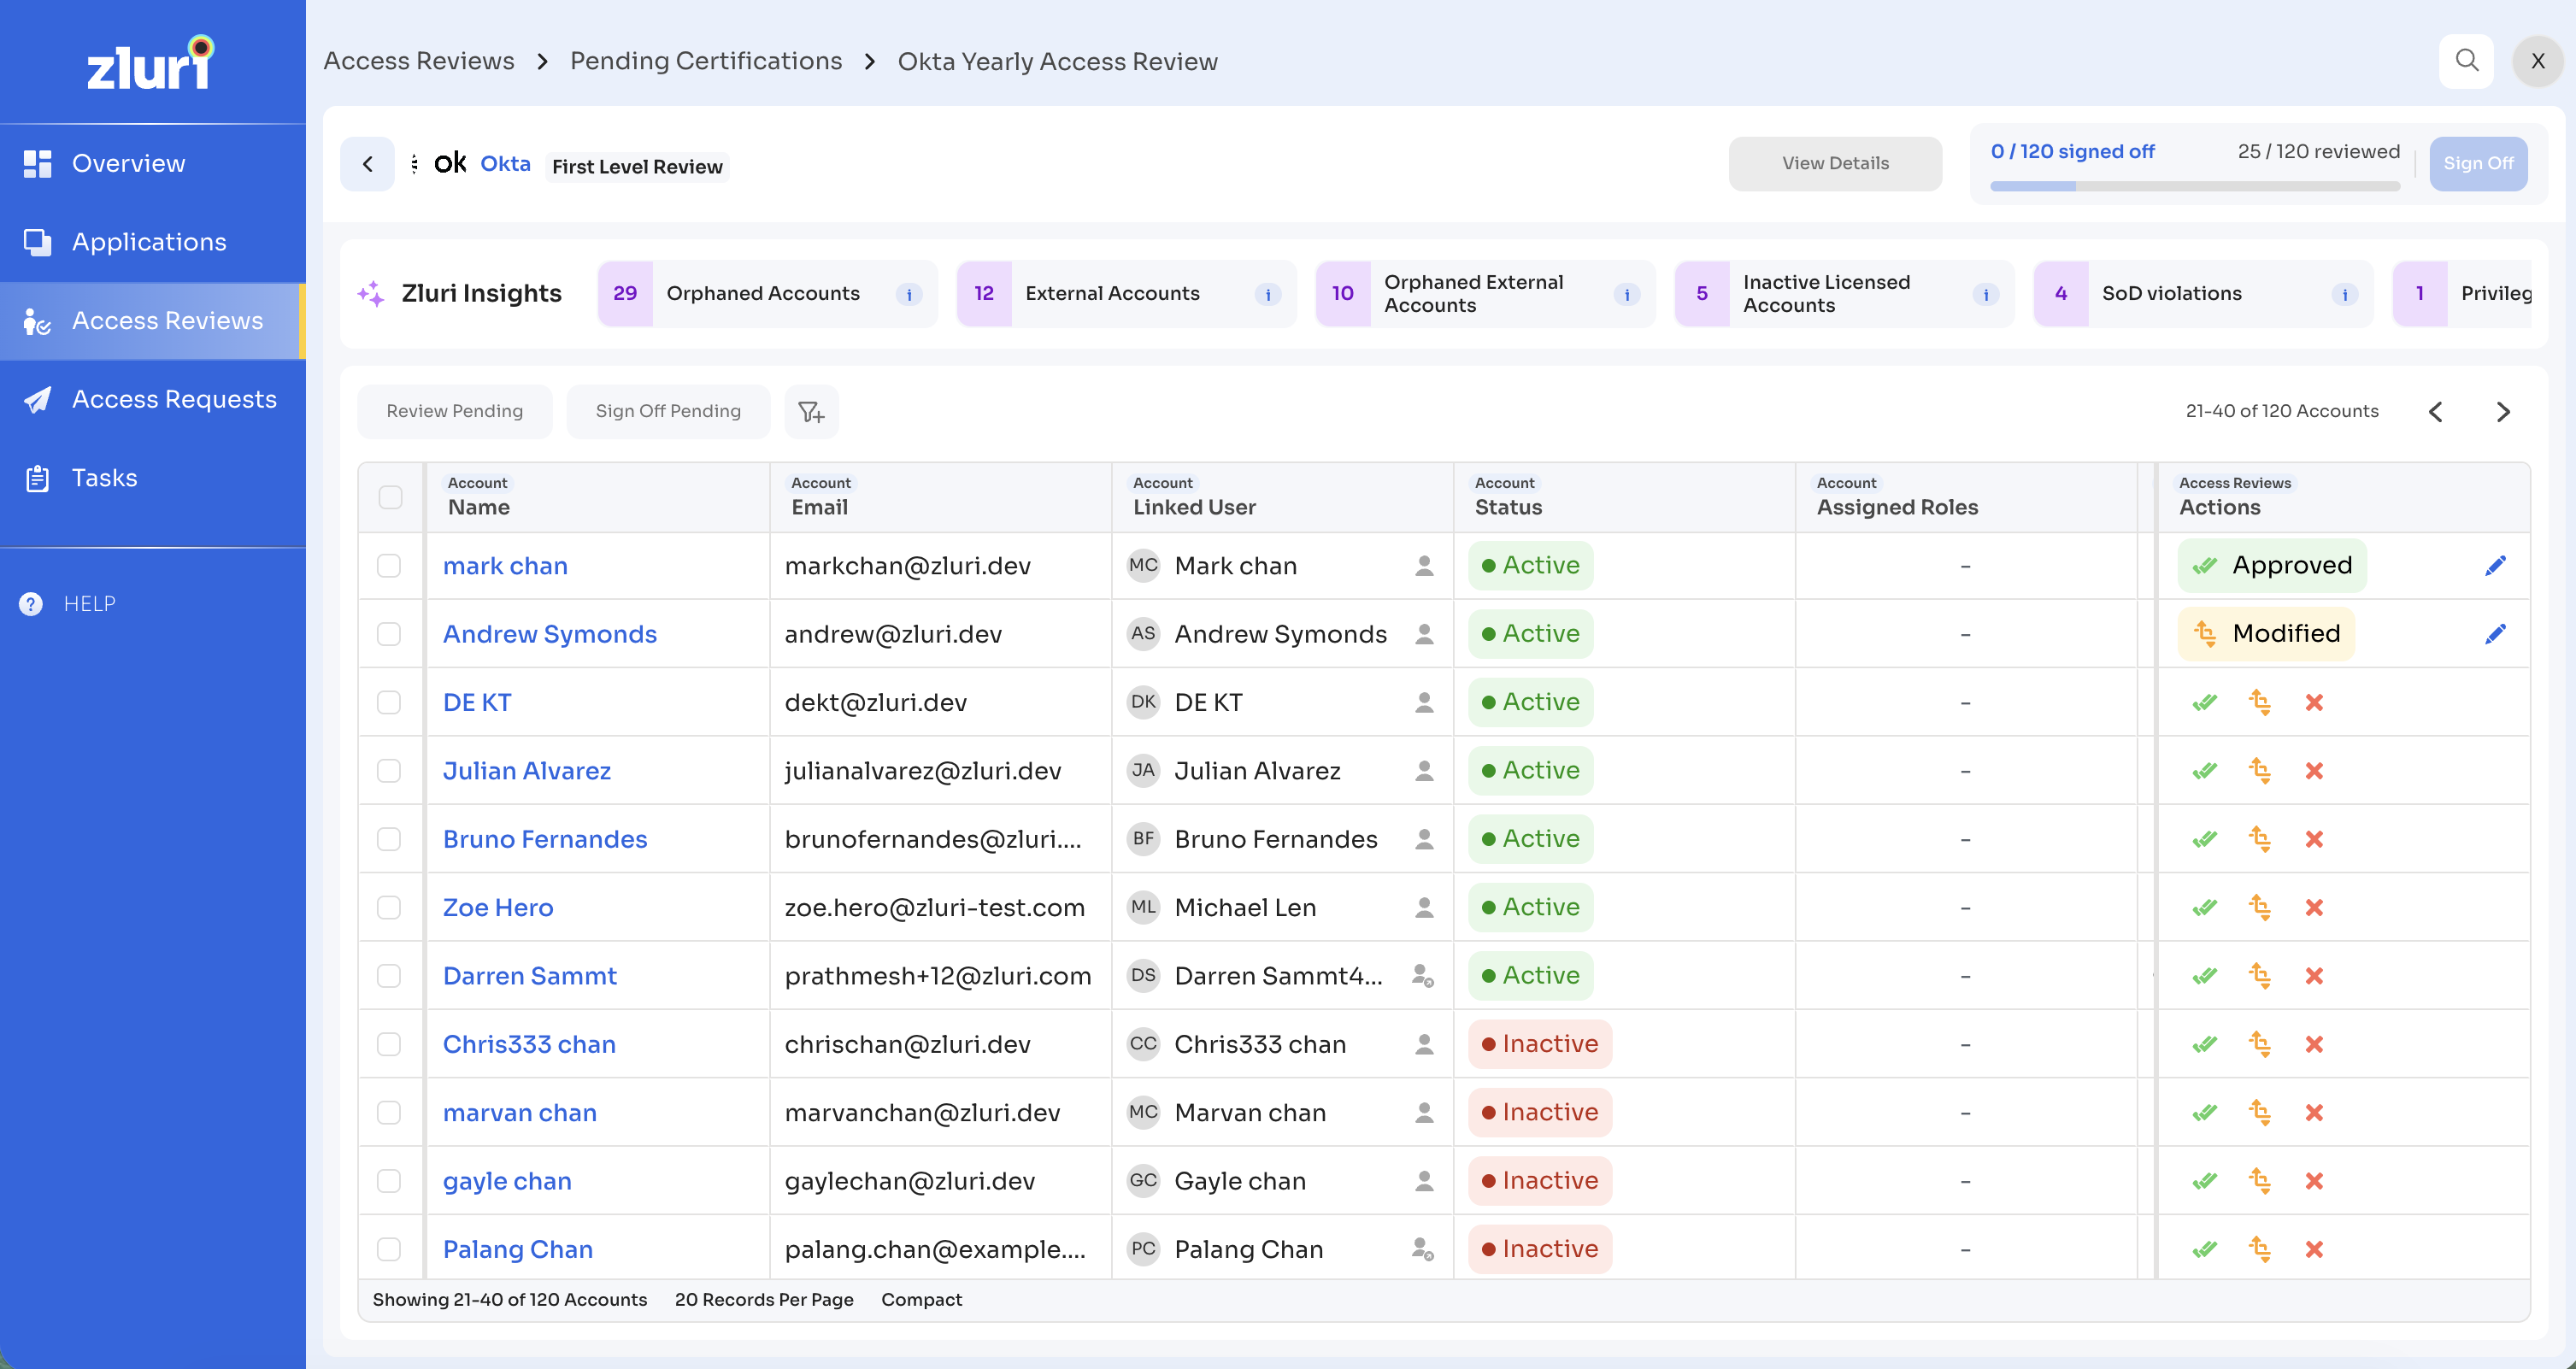
The UI for group reviews is slightly different. Instead of application roles, it shows group membership details.
-
The Entities column will display metadata like group source (e.g., Okta, Azure AD) and the number of users in the group.
-
Filters are available for group-related data, and reviewers will focus on whether users should stay in or be removed from the group, rather than their application access status.
-
3. Zluri Insights
Zluri provides automated insights to help reviewers prioritize records that may require closer attention during an access review. These insights act as signals for unusual or high-risk access patterns.
Examples of insights include:
- High-risk access assignments
- Users with inactive accounts but active access
- Access outliers based on app usage or department alignment
- Unusual privilege levels compared to similar roles
Insights are visually highlighted in the review table so reviewers can quickly identify records that need scrutiny.
In addition to flagging potential risks, Zluri also provides recommended actions where possible. For example:
- If a user is inactive but still holds a license, Zluri may recommend revoking access.
- If a user has a high-privilege role that seems inconsistent with peers, Zluri may recommend modifying access to a standard role.
- If the account is active and access usage aligns with role expectations, Zluri may suggest approving access.
These recommendations help reviewers make faster, more consistent decisions while reducing the chance of oversight.
Segregation of Duties (SoD) Violation Insights
For organizations with the Segregation of Duties module, Zluri also surfaces SoD violations as insights during a review. An SoD violation is a conflict between two entitlements rather than a property of any single one, so it cannot be identified from one access record on its own. Where the insights above indicate that access may be unusual, an SoD violation indicates that a specific policy defined by the organization has been breached.
No configuration is required, and there is no separate setting for Access Reviews. Once SoD policies are configured, violations appear in certifications automatically.
An SoD policy is defined in terms of the entitlements an account or a group holds. SoD violation insights therefore appear in certifications that review accounts or groups: app account reviews, user account reviews, and group reviews. They do not appear in app user reviews, where the records under review are a user’s aggregated application access rather than the underlying account.
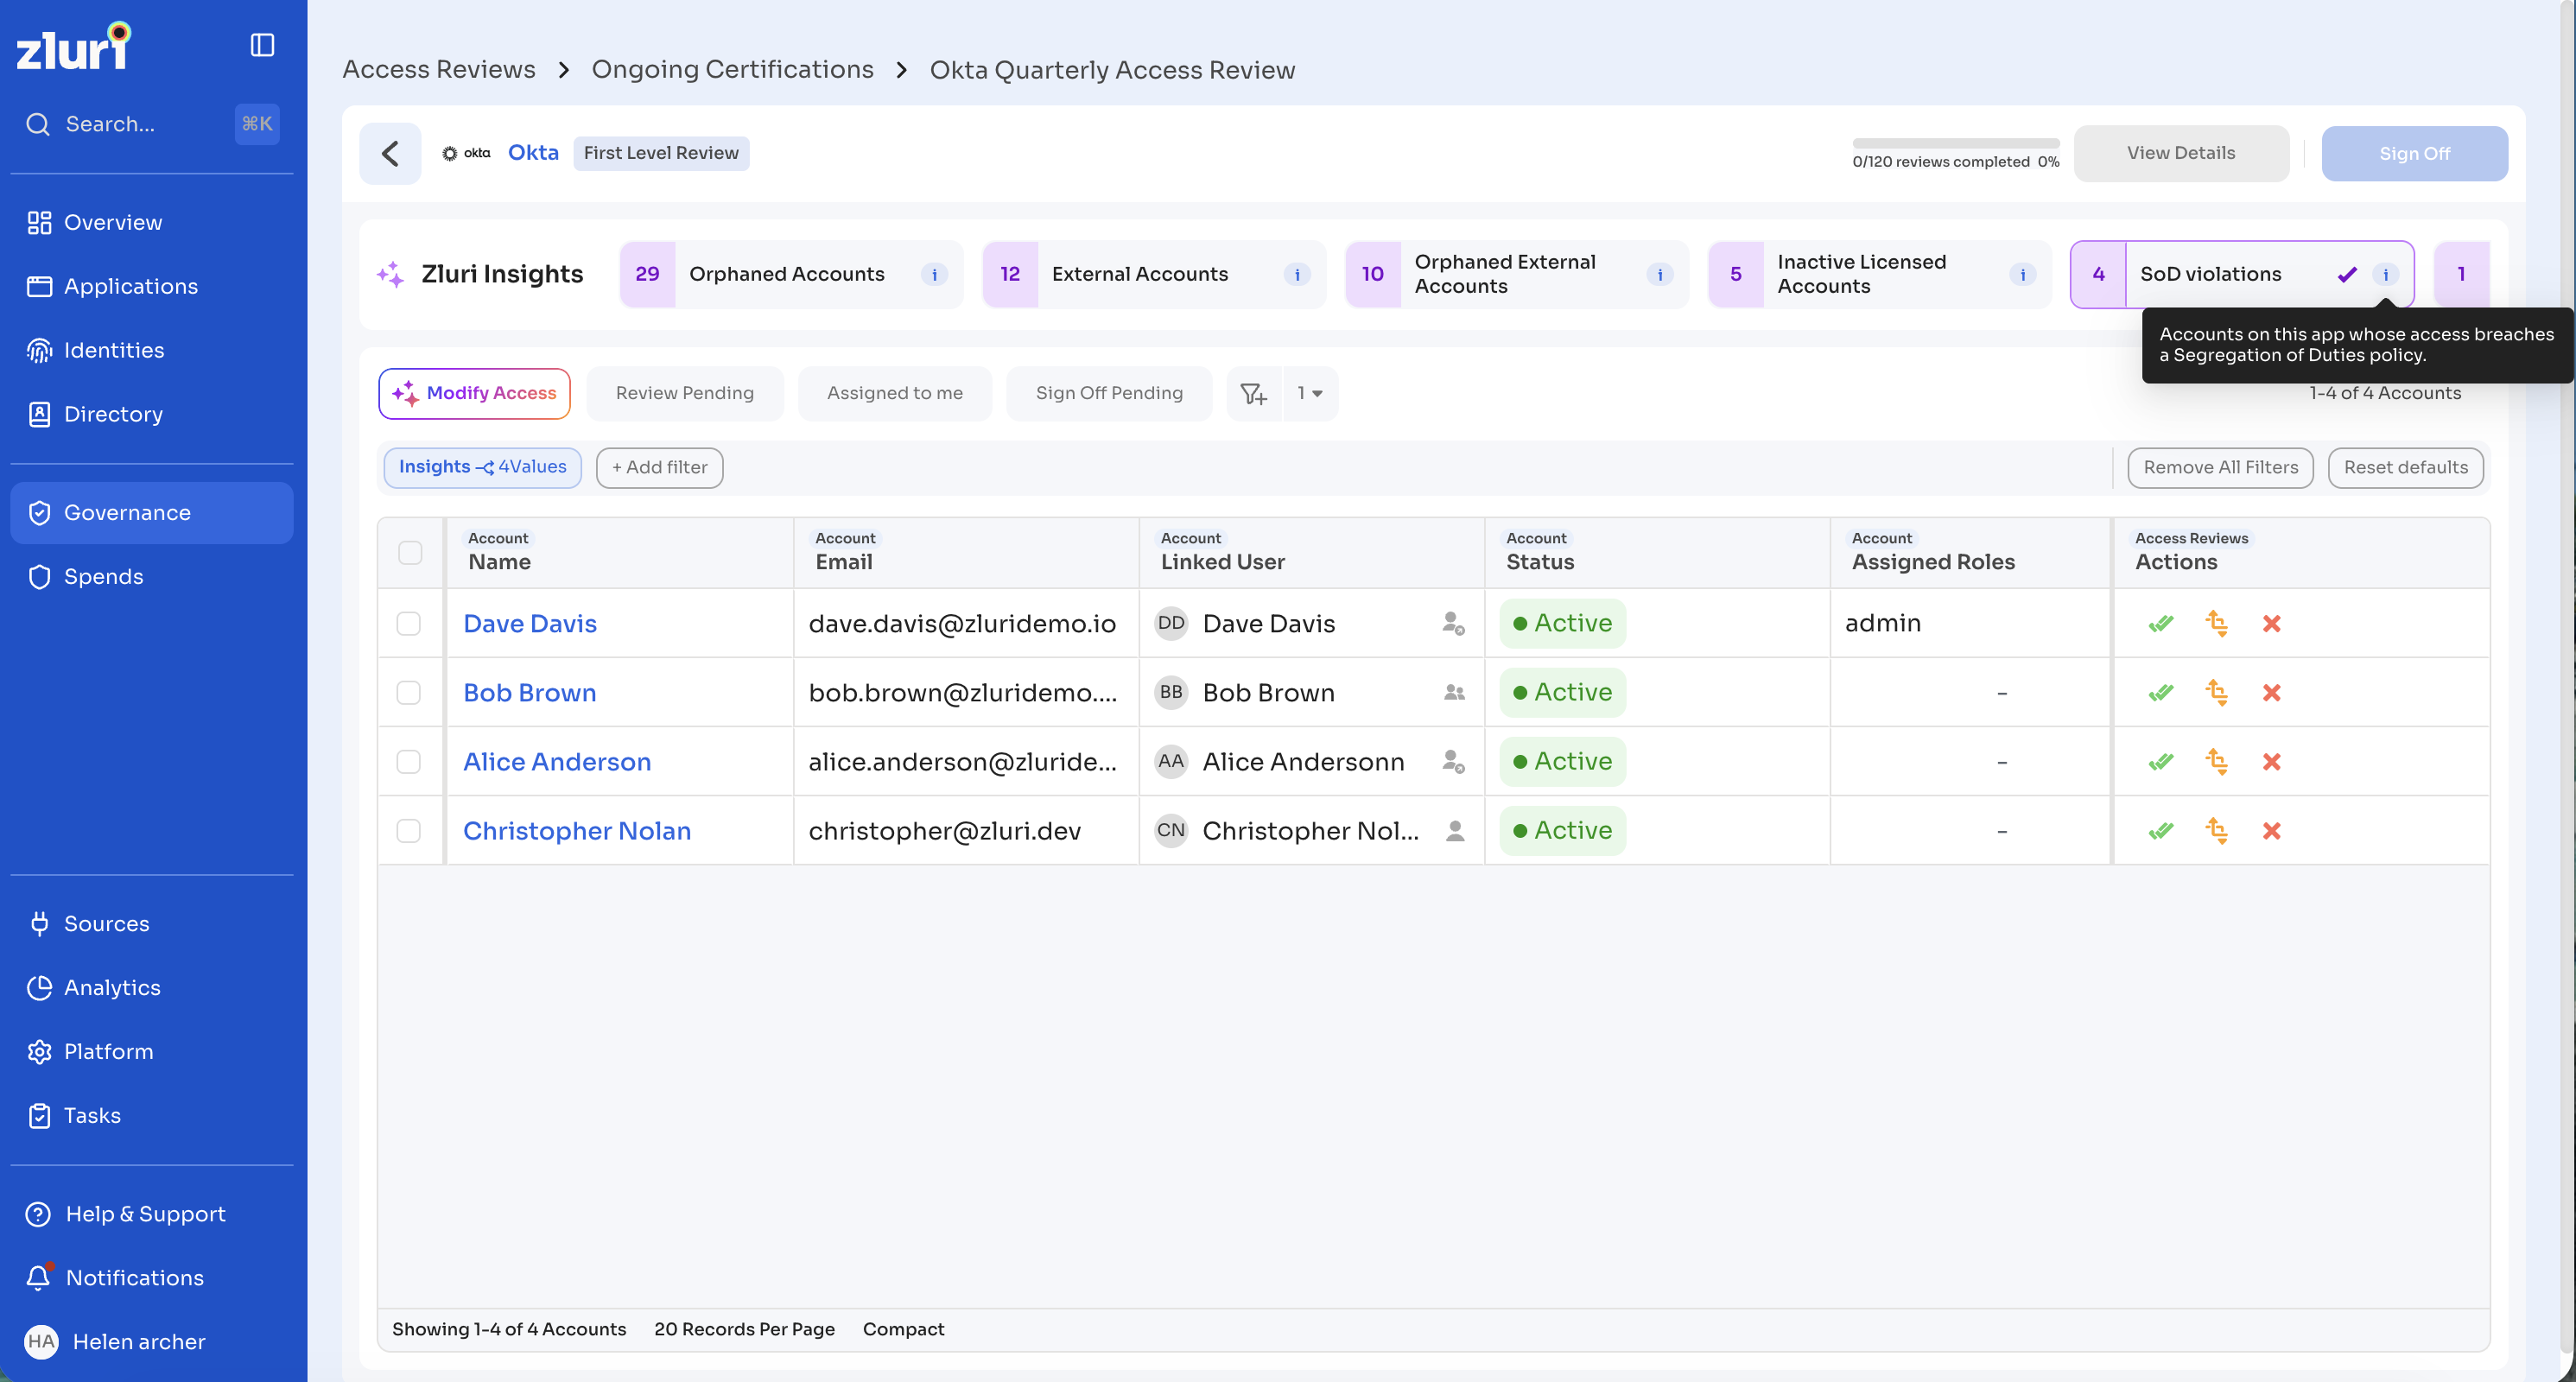
Zluri separates these into two insight types:
SoD violations: conflicts that are still open and need a decision.
SoD violations with Exemption: conflicts whose risk has already been formally accepted in the Segregation of Duties module. Reviewers can see the exemption but are not asked to decide it again.
Only these two states come into a certification. Violations that are resolved, closed, or pending verification do not appear, as they no longer represent live risk.
Every SoD violation carries a severity of Critical, High, Medium, or Low. Unlike the insights above, this rating comes from the policy definition set by the organization rather than being assigned by Zluri.
Zluri recommends an action for each violation type:
For an open SoD violation, Zluri recommends Modify, as a conflict is broken by adjusting one side of the combination rather than by removing the user’s access entirely.
For an SoD violation with Exemption, Zluri recommends Approve, as the risk has already been formally accepted.
Where a record carries several insights with different recommendations, the strongest recommendation applies. Revoke takes precedence over Modify, which takes precedence over Approve.
4. Reviewing Records
Once a certification and application or group are selected, the system displays a list of records that require review. The columns shown are based on the configuration defined by the Certification Owner. Reviewers can evaluate whether access should be approved, modified, or revoked based on the user’s role and access level.
Reviewing Users
After opening a certification and selecting an application, the system displays a list of records that require review. The columns shown in this table are configurable and vary based on what the certification owner selected during setup.
Common Column Types
The columns displayed in the review table depend on how the Certification Owner configured the certification.
- For application reviews, columns typically include app-specific attributes such as roles, licenses, or last login.
- For group reviews, columns focus on user-related attributes like employment status, department, or group role since app-specific fields are not relevant.
Examples of commonly seen columns:
- User Name
- User Email
- Employment Status
- Application Access Status (for apps)
- Assigned Licenses (for apps)
- Department
- Role / Group Role (depending on entity type)
- Last Login (for apps)
Available Actions
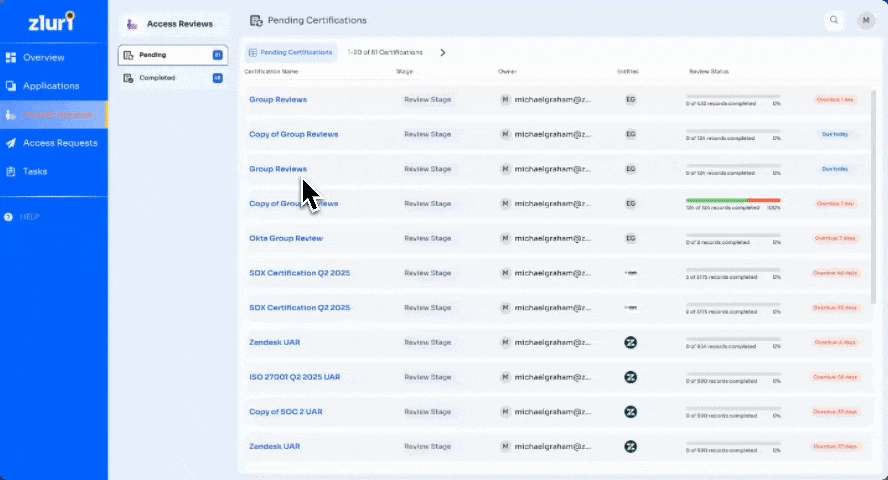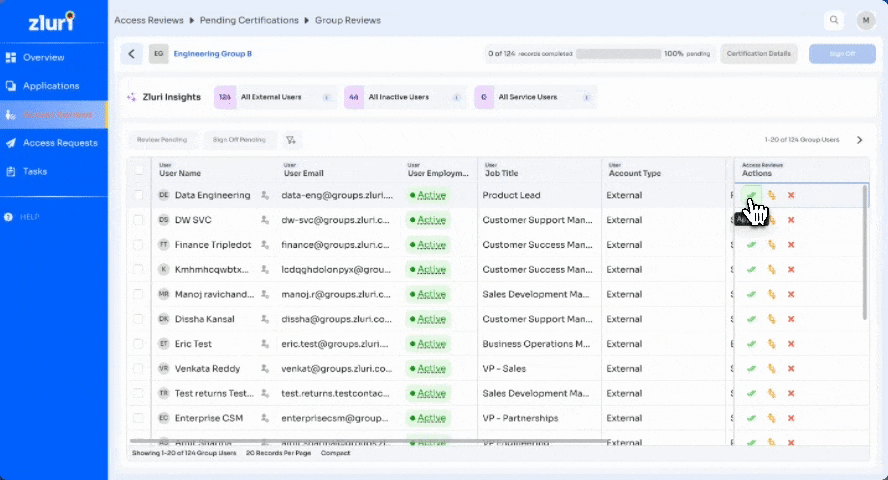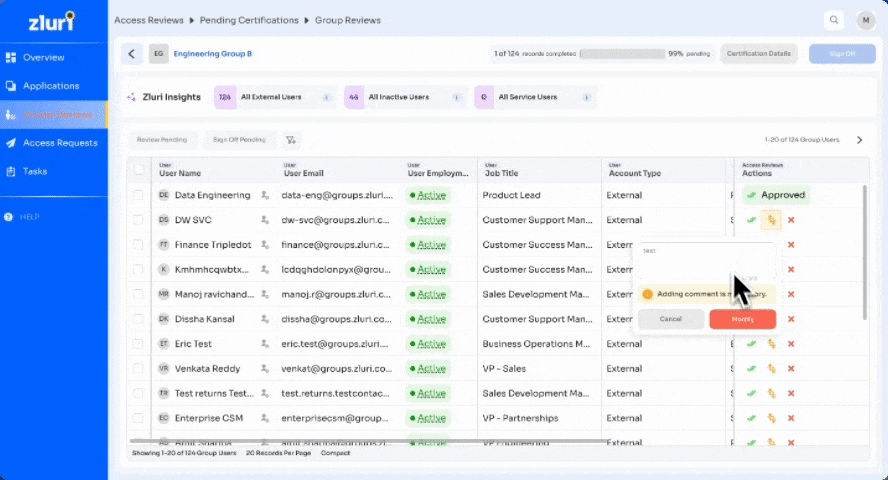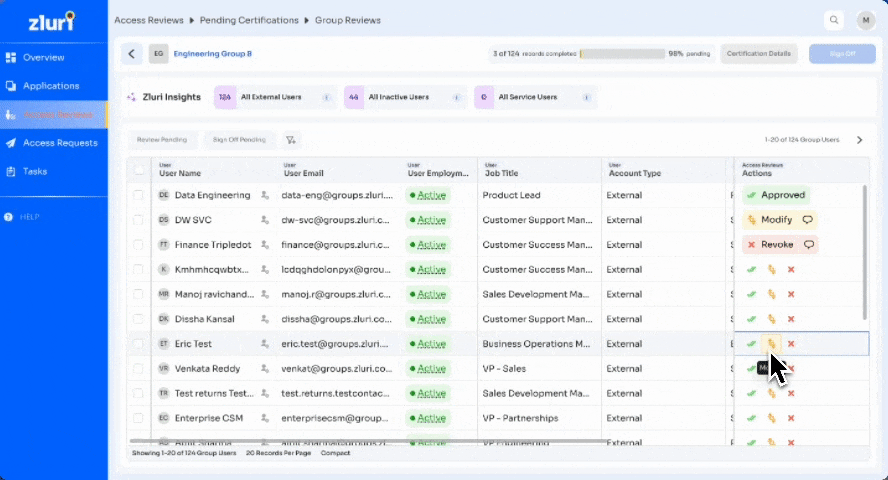
In the Actions column, three icon-based options appear for each record:
- Approve
- Action: Confirms that access should be retained.
- Comment: Optional.
- Outcome: Selecting Approve saves the review immediately.
- Modify
- Action: Indicates that access needs to be changed or downgraded (e.g., revoke admin role, downgrade license type).
- Comment: Mandatory, with details of the required changes.
- Outcome: The Modify button remains disabled until a comment is entered.
- Revoke
- Action: Indicates that access should be fully removed.
- Comment: Mandatory, with justification for revocation.
- Outcome: Selecting Revoke finalizes the decision.
Using Insights & Recommended Actions
Alongside these action options, Zluri Insights may highlight specific records as high-risk or unusual based on factors like:
- Inactive users who still hold app access.
- Access outliers (e.g., user with a role not common in their department).
- High-privilege assignments.
- Misaligned access vs. app usage patterns.
For flagged users, Zluri may also display recommended actions (e.g., “Revoke unused access,” or “Downgrade license to standard”).
Reviewers can use these insights and recommendations to guide decisions more confidently, ensuring faster triage of high-risk access without having to analyze every record from scratch.
Viewing SoD Violations on a Record
Where the organization has the Segregation of Duties module, two further insights appear in the Zluri Insights bar at the top of the certification: SoD violations and SoD violations with Exemption, each with a count. Selecting either one filters the review table to the matching records.
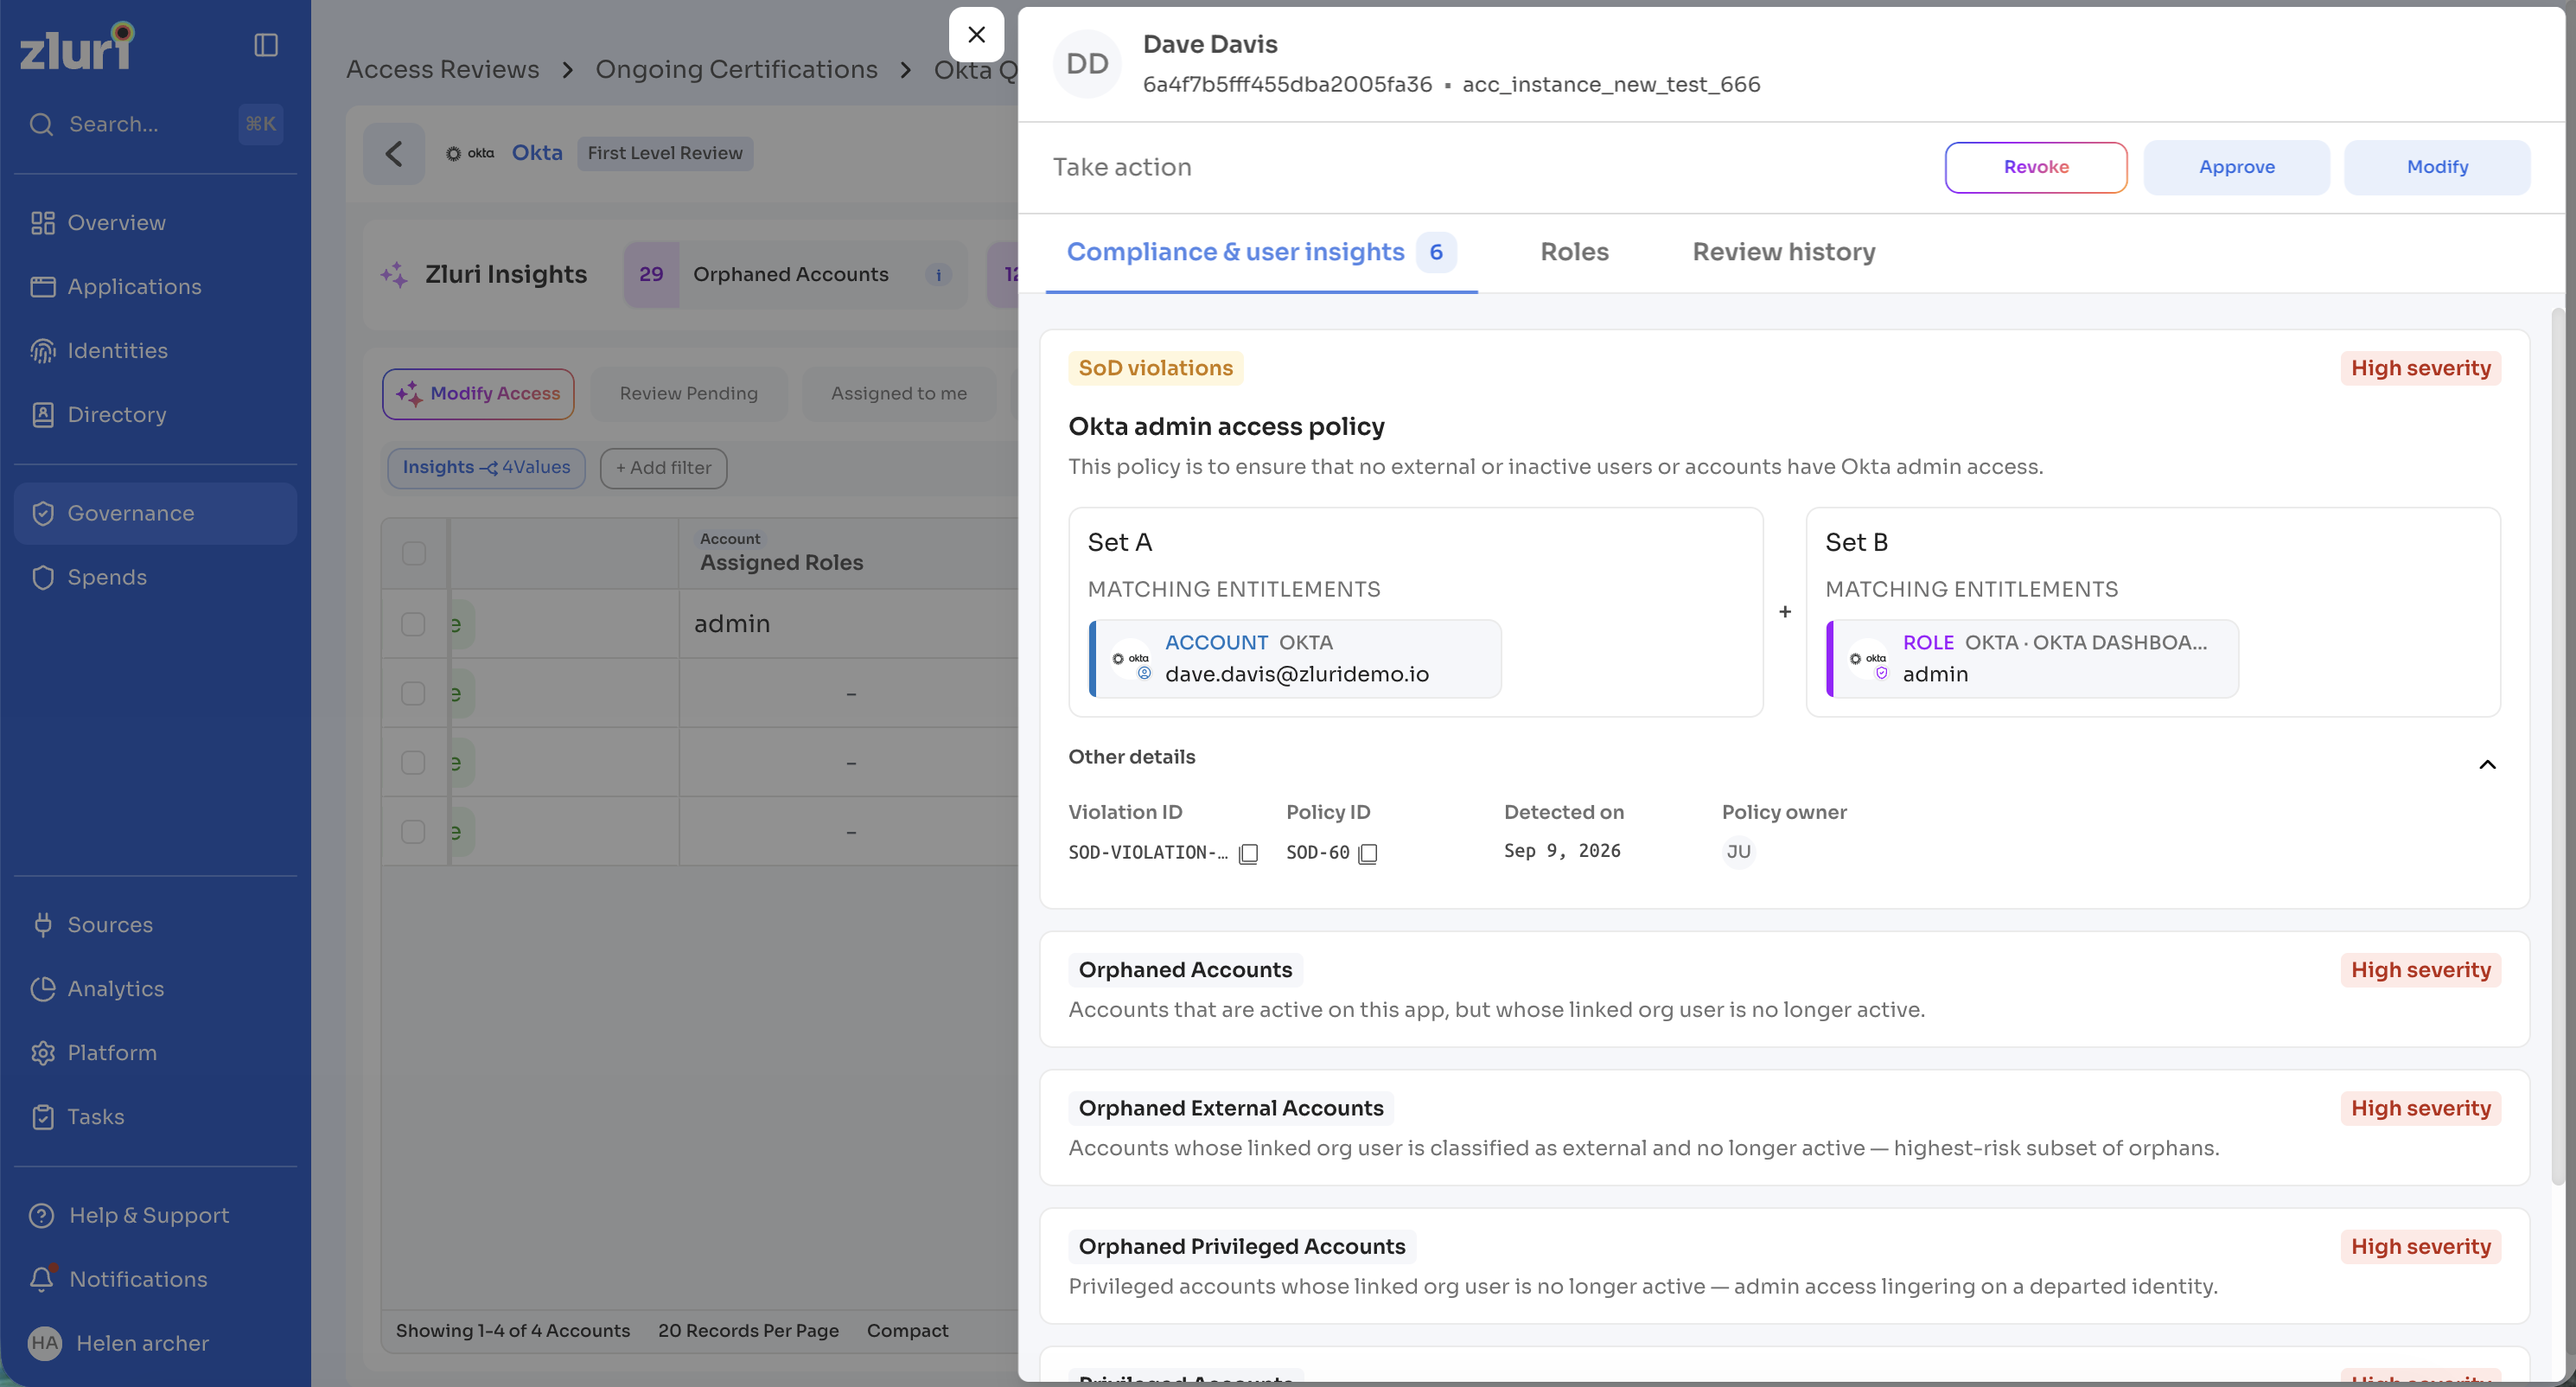
The review table also includes an Insights column showing a count of every insight on each record, covering SoD violations and the insights above together (e.g., “6 insights”). Selecting the count opens the detail panel for that record.
The panel opens on the Compliance & user insights tab, which lists every insight in order of risk: SoD violations first, then exempted violations, then the remaining insights. Revoke, Approve, and Modify appear at the top of the panel so reviewers can act without scrolling, with the recommended action highlighted. The panel also holds a Roles tab and a Review history tab.
Each SoD violation card shows:
Policy name and description.
Severity, taken from the policy definition.
Set A and Set B, the two sides of the conflict, each listing the matching entitlements. A set can match on an account, a group, a role, or a permission, so a conflict is not always one role against another.
Other details, which expands to show the policy ID, the date the violation was detected, and the policy owner. Reviewers who want to question a violation can contact the policy owner shown here.
Filtering by Policy
Under the Insights category in the filter panel, each SoD insight type expands into the list of policies that have violations in that certification. Reviewers can select one or more policies and apply the filter to narrow the table to those violations only. The applied filter appears as a pill above the table naming the insight type and the selected policy.
Notes:
- Real-time Saving: Review decisions are saved in real-time. As reviewers make decisions (approve, modify, revoke), changes are immediately recorded.
- Mandatory Comments: A comment is required for Modify and Revoke actions. If no comment is entered, Zluri will display a warning and disable submission.
- Editing Review Actions: All actions can be edited until the reviewer signs off. Once signed off, they are locked.
- Review Type Determines Availability: SoD violation insights appear in app account reviews, user account reviews, and group reviews. They do not appear in app user reviews.
- SoD Data is Fixed at Creation: A certification loads the open violations that exist at the moment it is created, and that set does not change for the life of the certification. Violations detected afterwards, and policy changes made afterwards, do not affect a certification already in progress.
- Exemptions are Read-only in a Review: Reviewers can see that risk was accepted, but exemptions are recorded in the Segregation of Duties module, not during a review.
- Conflicts Appear on Participating Rows Only: A conflict between a Slack entitlement and a GitHub entitlement appears on that user’s Slack row and GitHub row, and not on rows for unrelated applications.
- All Enabled Policies Apply: Every enabled SoD policy is evaluated for every certification in this release.
5. Bulk Selection & Editing
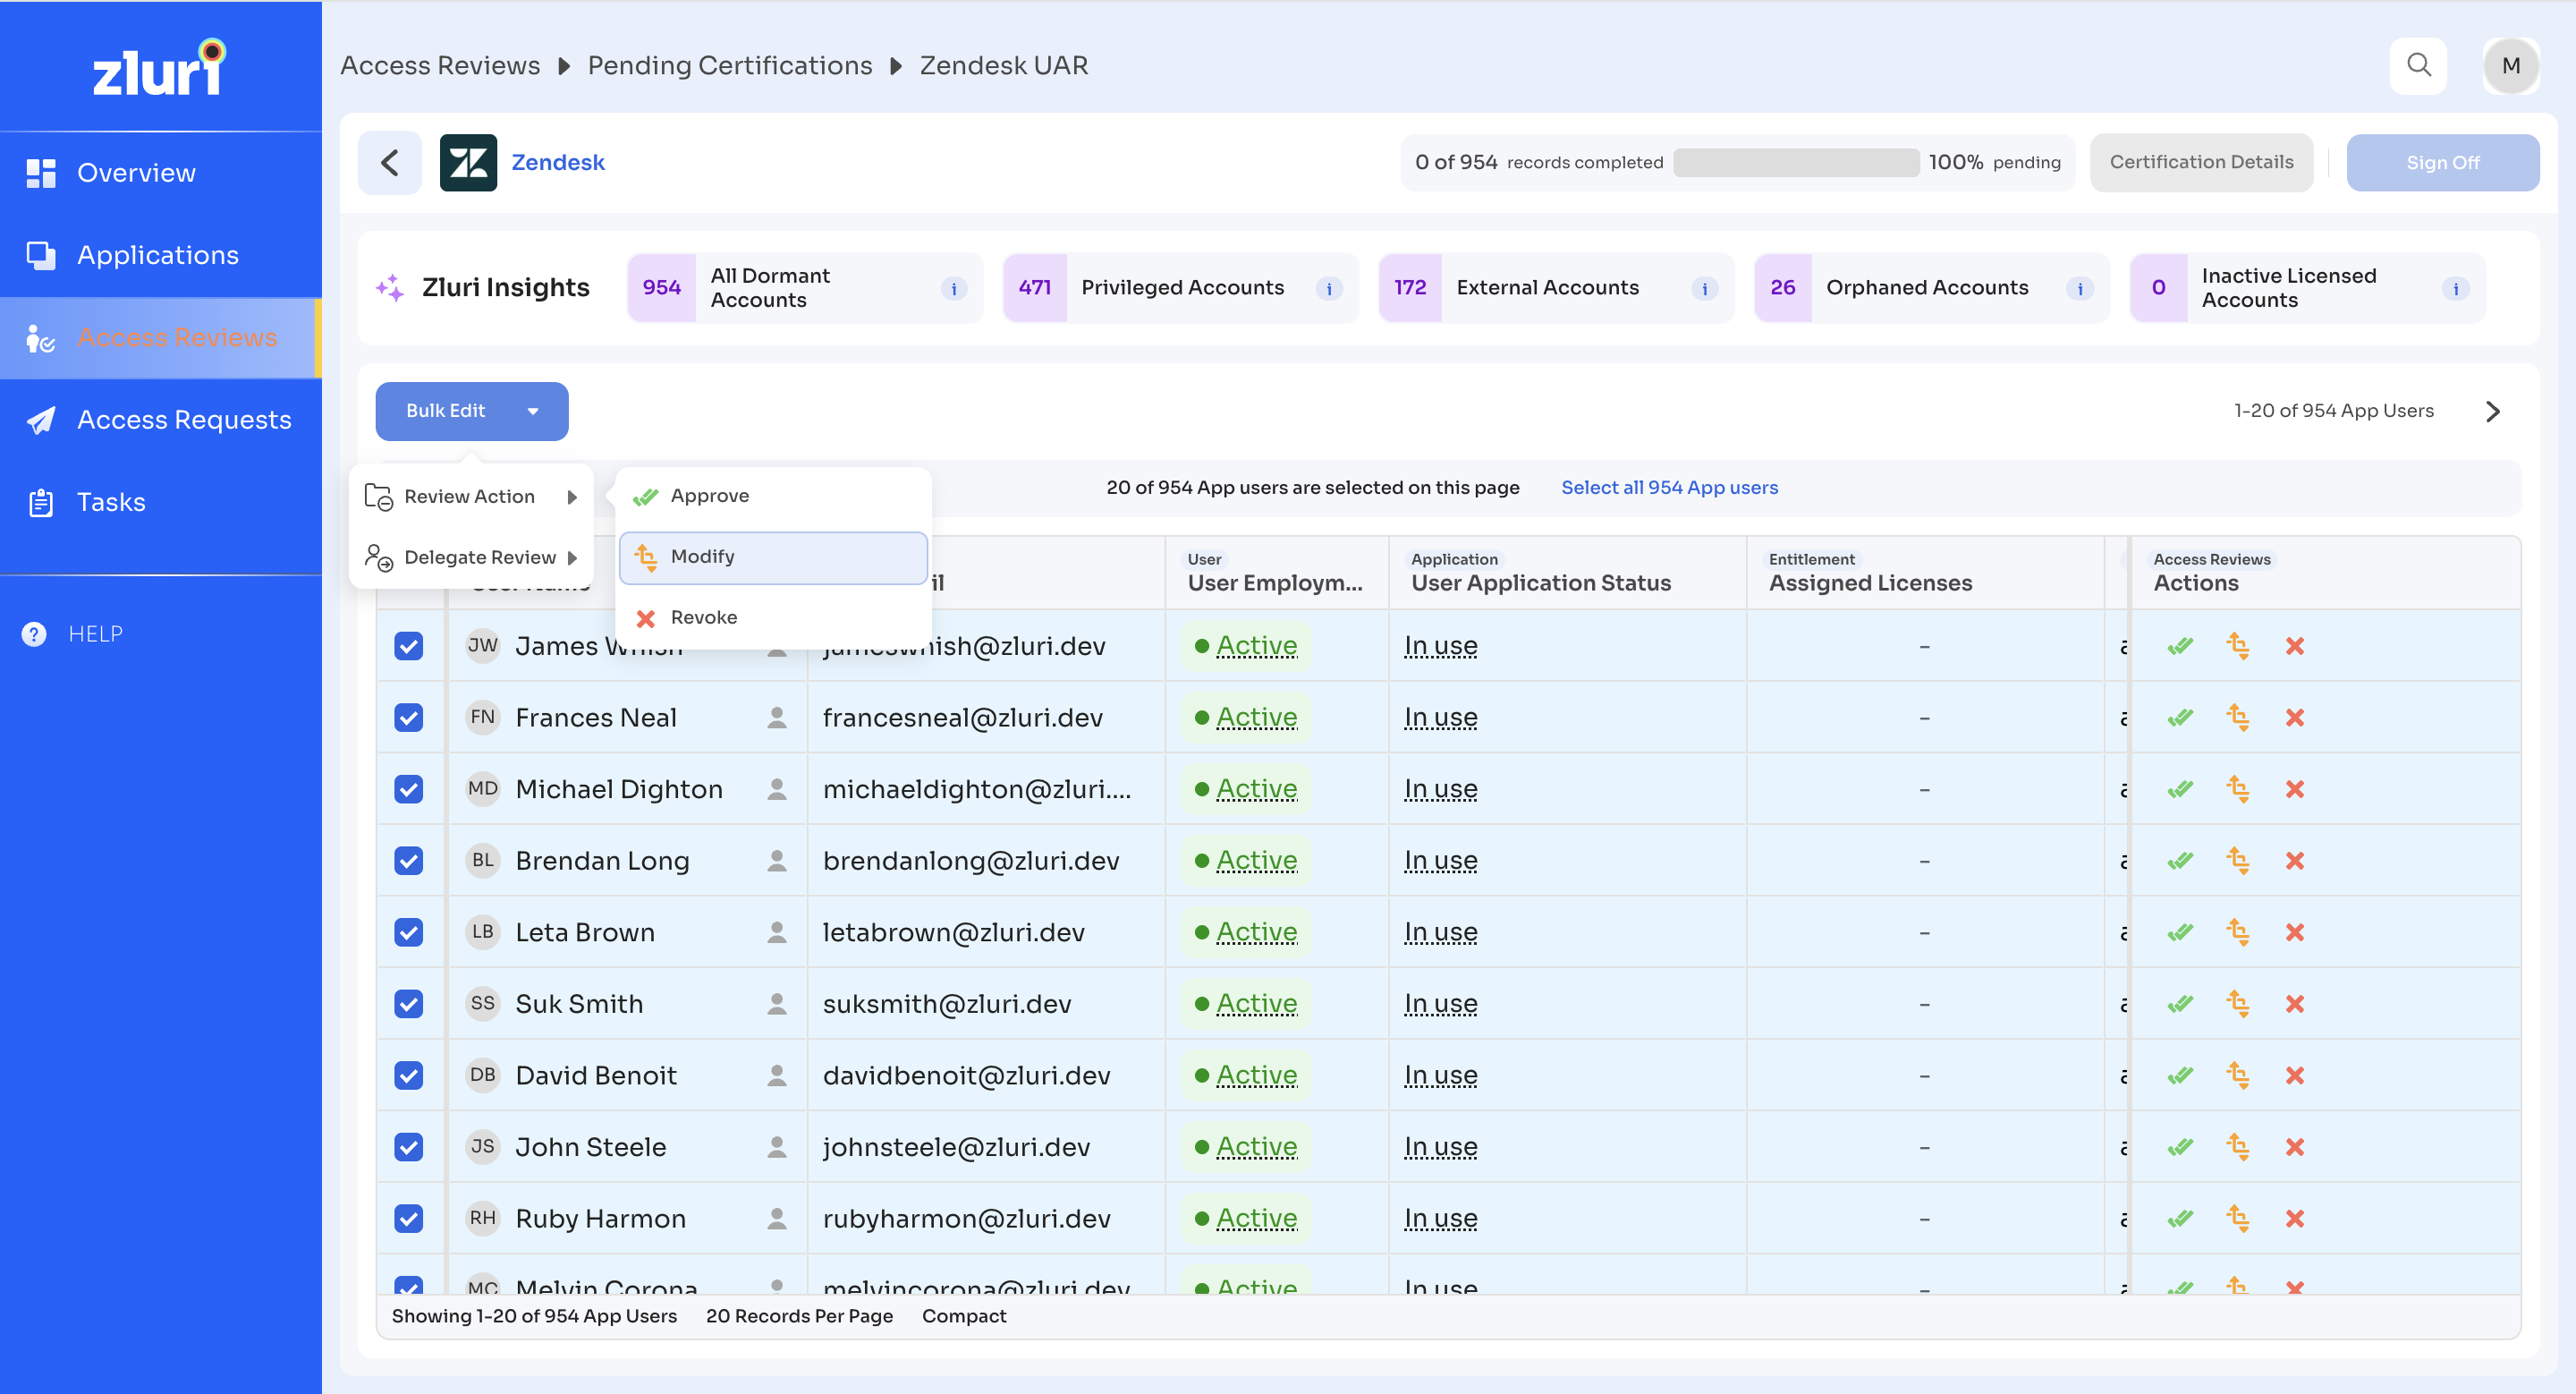
Zluri allows reviewers to update review actions for multiple users simultaneously using bulk selection. To do this:
- Select records using the checkboxes in the first column of the table.
- Once one or more records are selected, the Bulk Edit menu appears at the top of the table.
- Choose the desired action: Approve, Modify, or Revoke.
- If Modify or Revoke is selected, a mandatory comment is required and applied to all selected rows.
- Select Save to apply the changes in bulk.
Bulk edit ensures consistency for users with similar access patterns and helps reduce repetitive manual steps. All bulk updates are recorded with the same audit trail as individual actions.
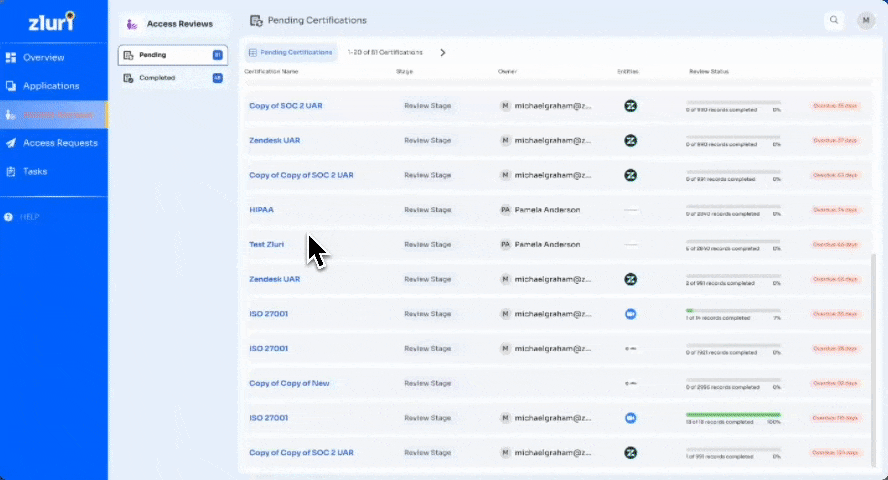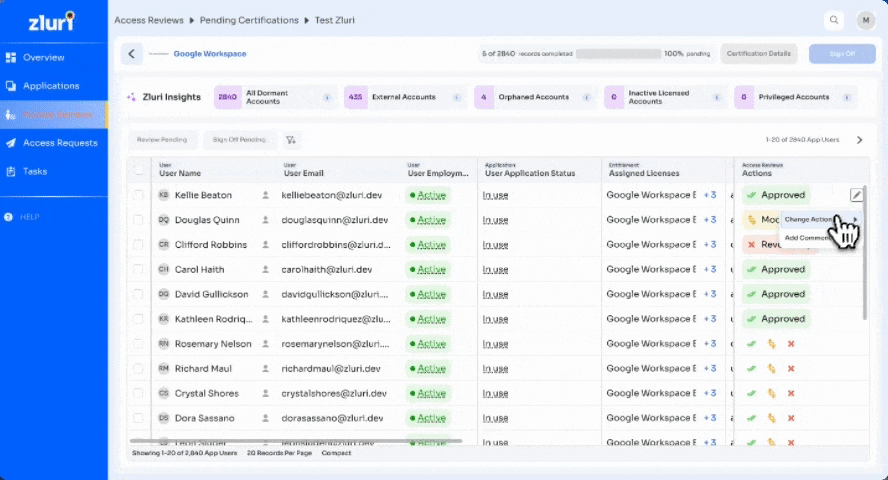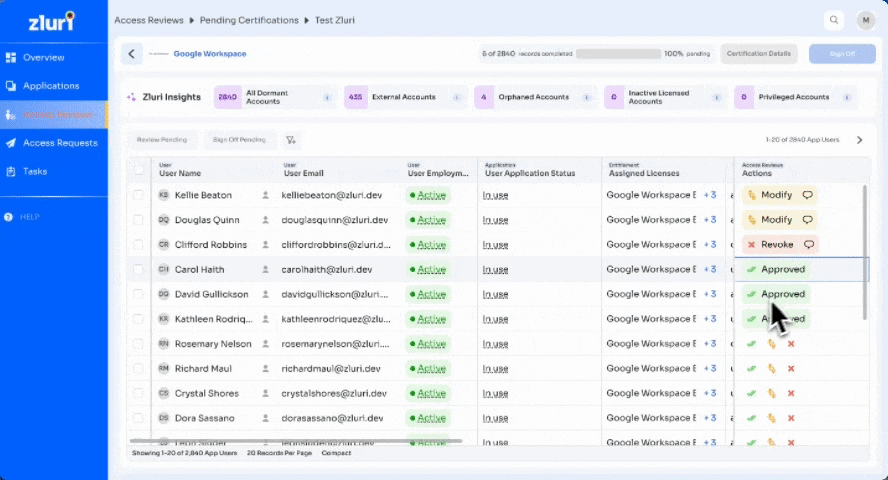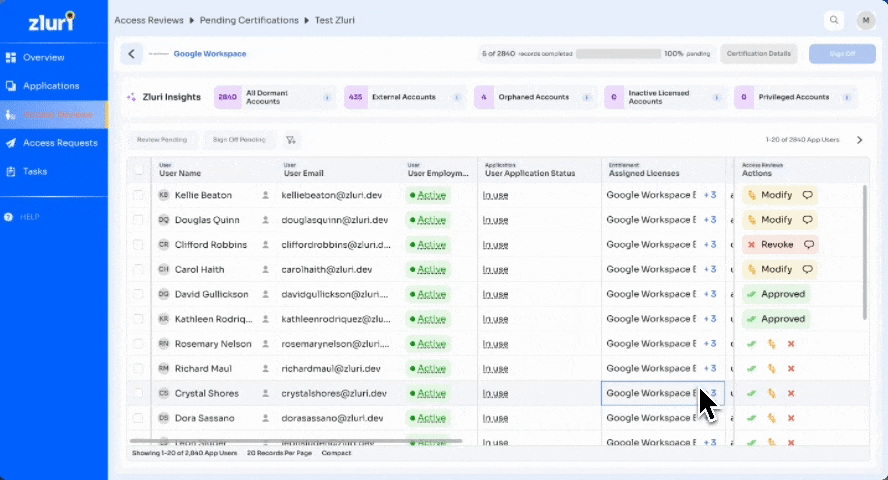
6. Editing Review Decisions
Reviewers can update previously submitted review actions for any record until they sign off.
To Change a Review Action:
-
Locate the user row with an existing action (e.g., Approved, Modify, Revoke).
-
Hover over the action badge to see the Edit (✏️) icon.
-
Select the Edit icon.
-
In the dropdown menu, select Change Action.
-
Choose a new action:
- Approve
- Modify
- Revoke
-
Enter a mandatory comment justifying the change.
-
Select Save to confirm the updated action.
Notes:
- Comments are always required when modifying an existing action.
- All changes are captured in the activity trail and included in the final certification report.
- Edits are only allowed before sign-off. Once signed off, records become locked and cannot be changed.
7. Delegating Reviews
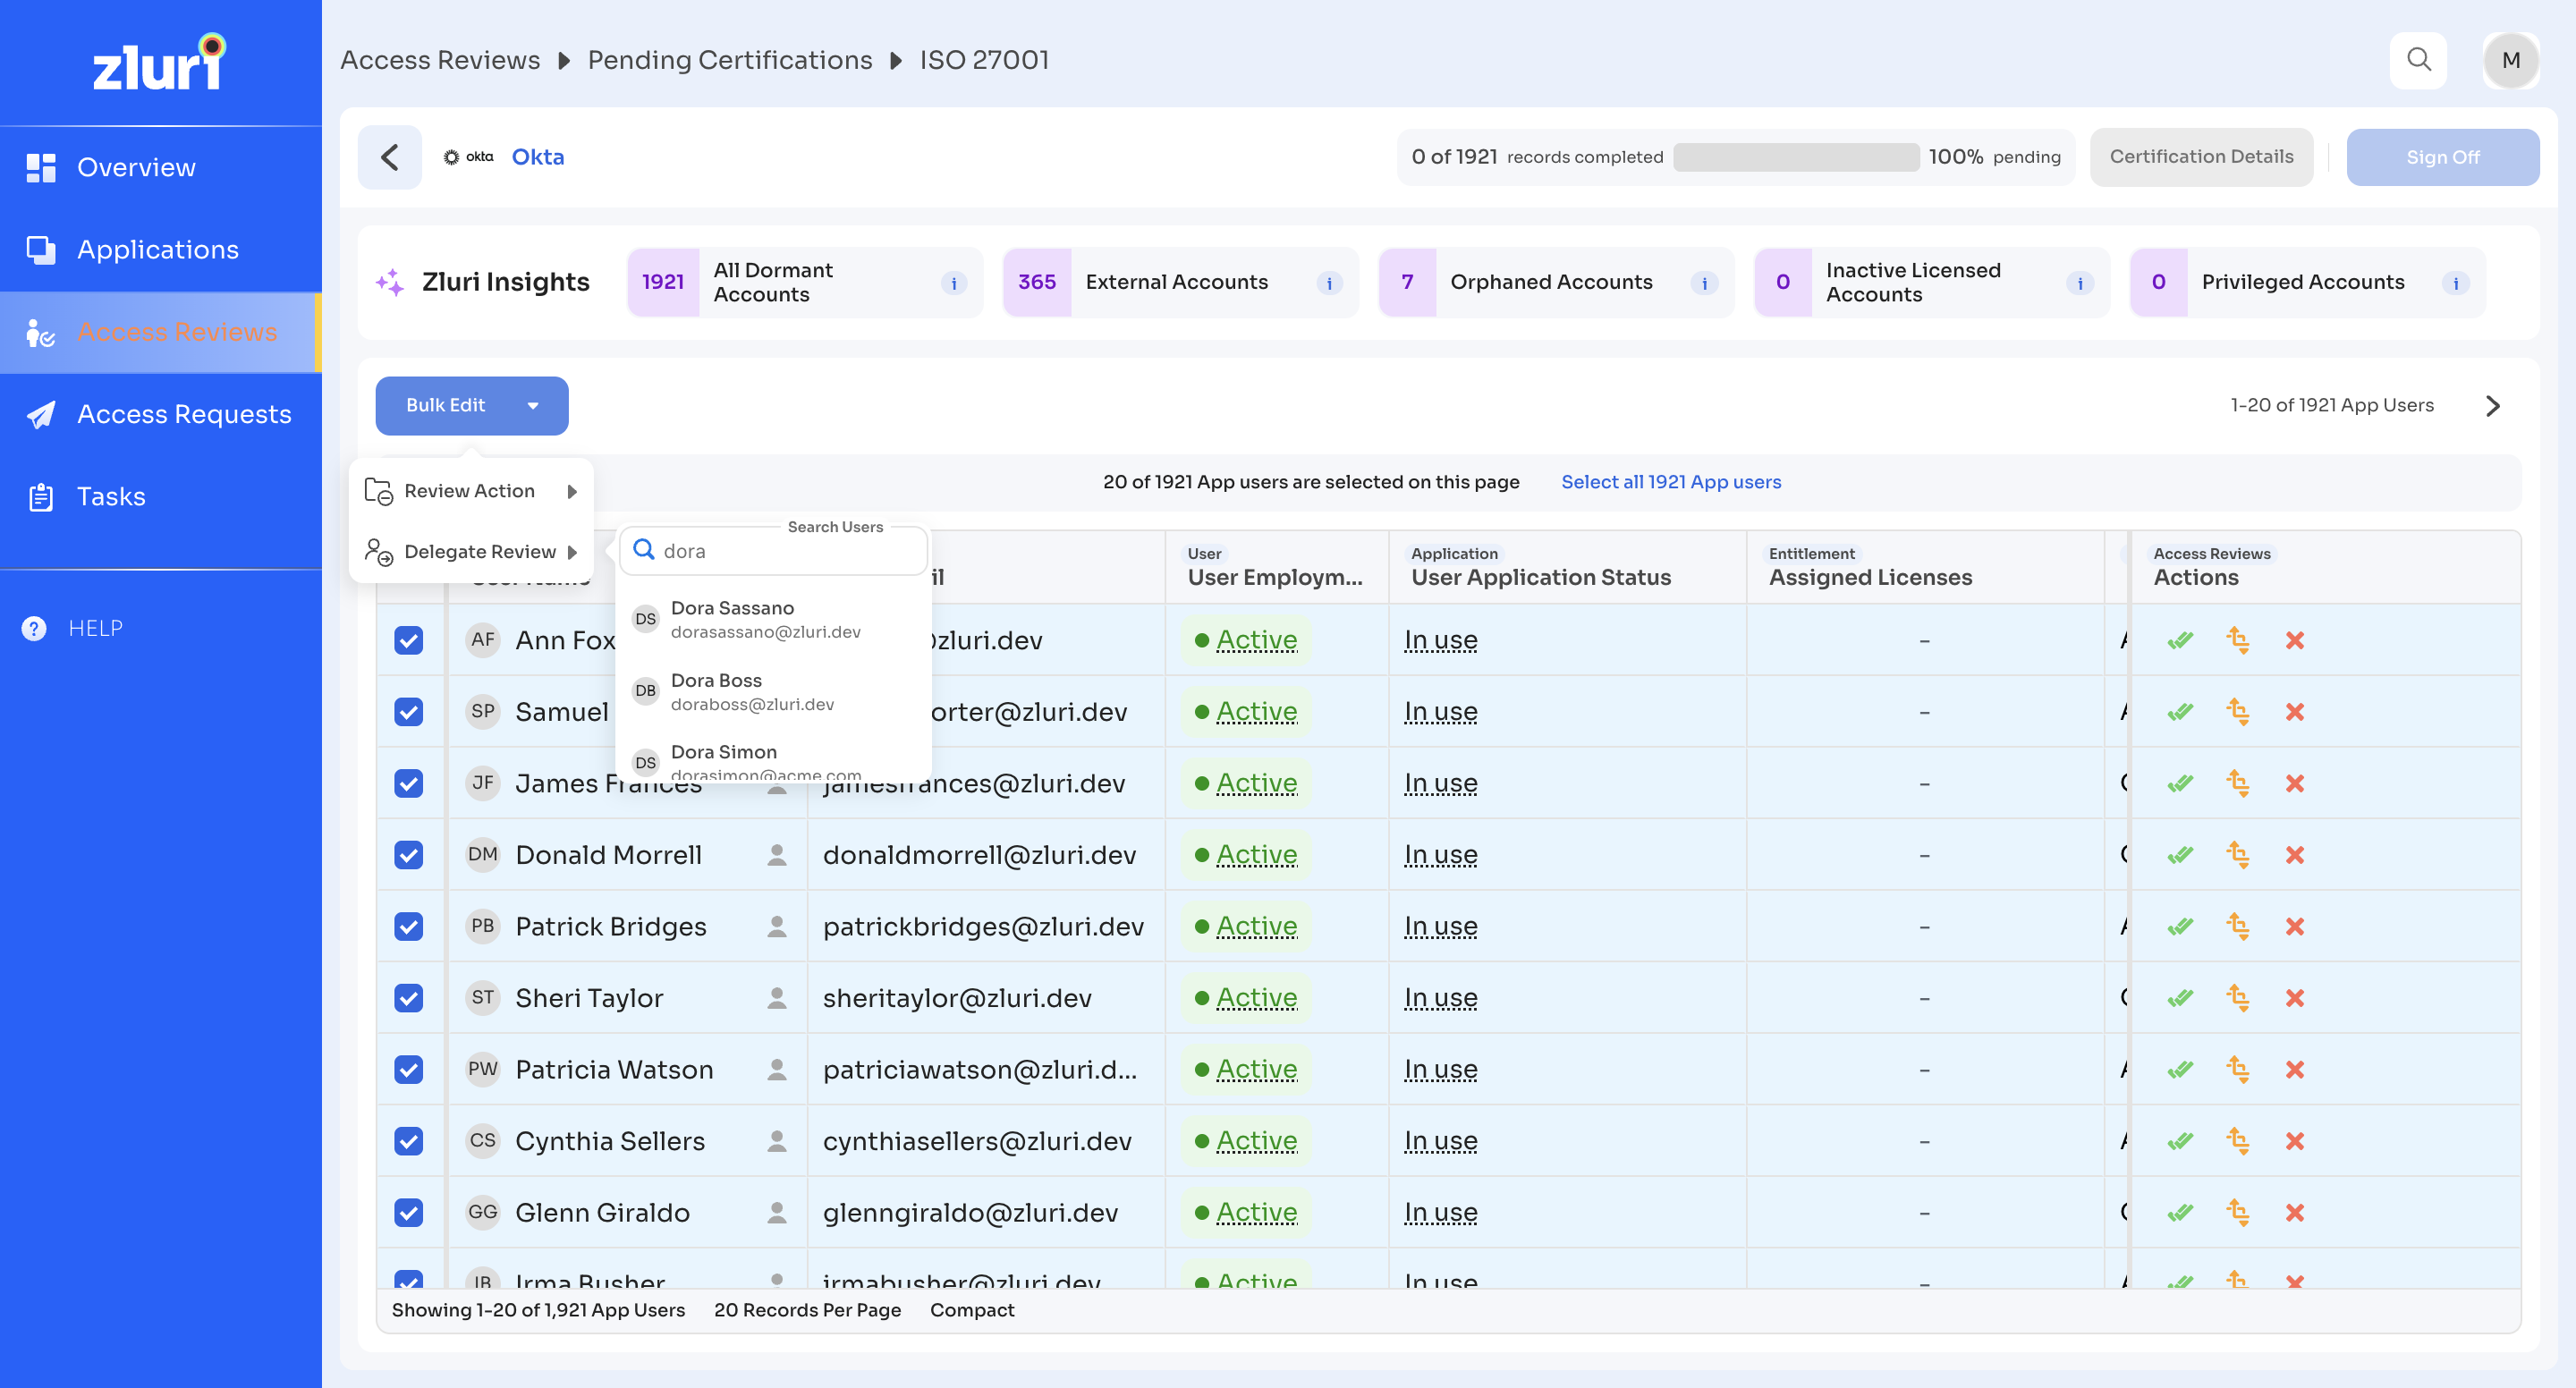
Zluri supports delegation of access review records through bulk delegation. This feature helps reassign responsibility when the original reviewer is unavailable or when specific records require input from a different stakeholder.
Bulk Delegation
To reassign reviews for multiple users at once:
- Select records using the checkboxes in the leftmost column.
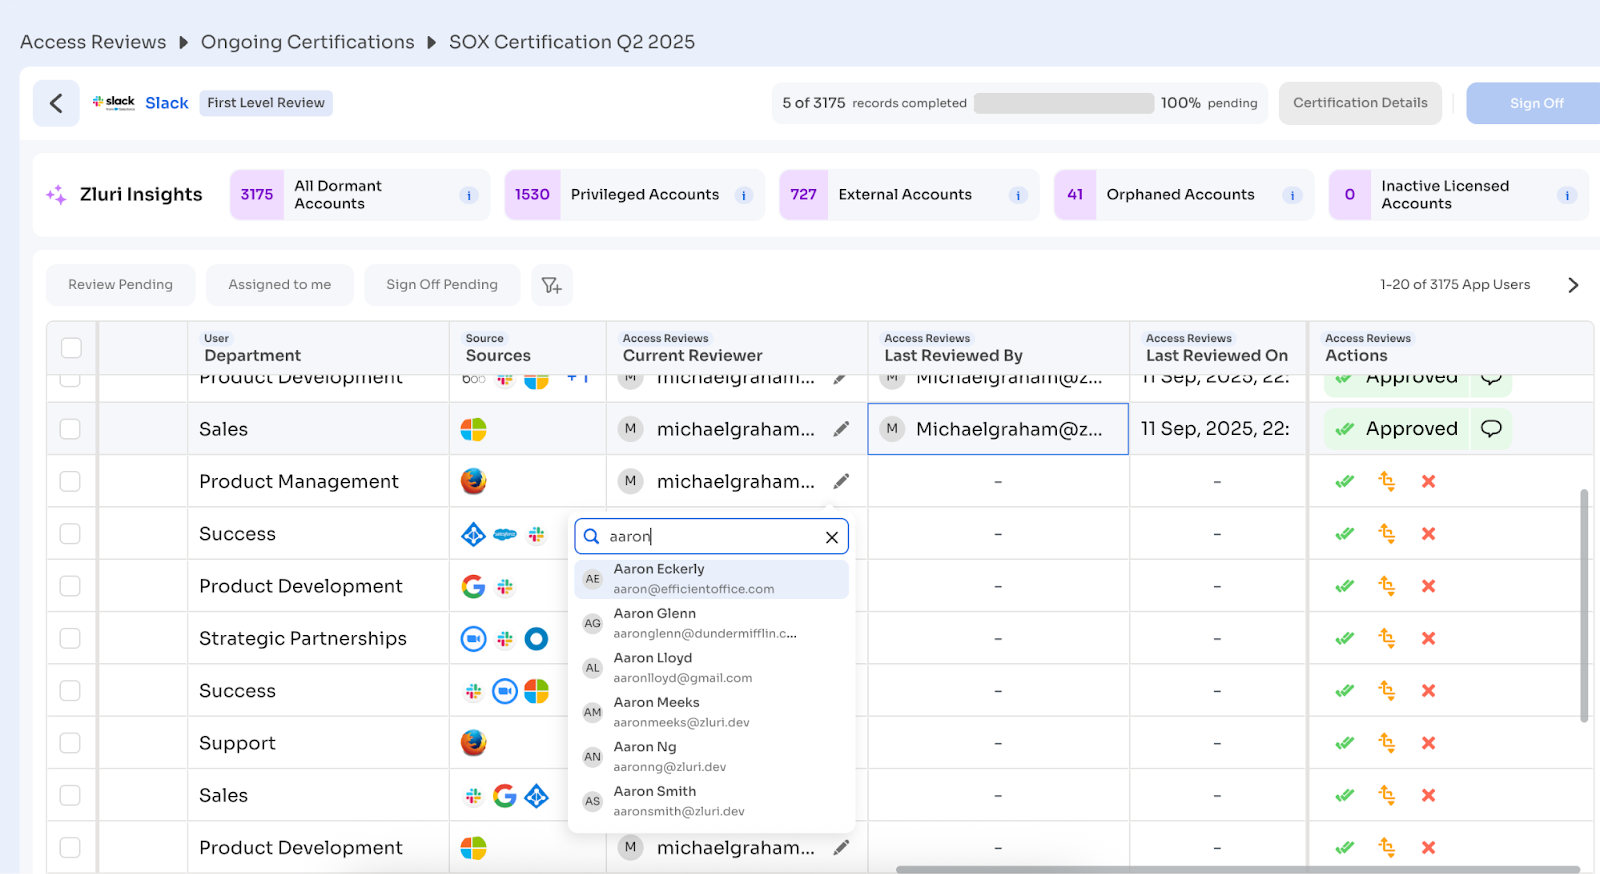
- Select Bulk Edit at the top-left of the table.
- Select Delegate Review.
- Use the search bar to find and assign the new reviewer.
- Confirm by selecting Continue.
Notes
- Only Pending reviews that are yet to be signed off can be reassigned.
- Delegation can be performed by the assigned reviewer or the certification owner or Admins with Owner, Admin, or IT Admin roles (or custom Access Reviews permissions, if enabled) can also perform this action.
- After delegation:
- The original reviewer no longer sees the reassigned records.
- The new reviewer sees the delegated records in their review task list.
- Audit logs capture the delegation action and updated reviewer identity.
8. Signing Off
After completing all assigned review actions for a certification, reviewers must finalize their inputs by signing off.
Reviewed vs Signed Off
Reviewing a record and signing it off are two separate actions. Selecting Approve, Modify or Revoke records a decision against a record. Signing off confirms every decision for that application or group and hands the certification on. A certification progresses to remediation or to the next review level only after sign-off, so records that carry a decision but no sign-off hold the certification in place.
Zluri shows both counts wherever progress appears. The signed off count leads, in blue. The reviewed count appears beside it, in grey. Both count records against the same total, and the signed off count is never higher than the reviewed count.
The bar beneath the counts splits into three parts:
- Reviewed and Signed Off (solid blue) – The reviewer decided the record and confirmed it. These records are locked and cannot be edited.
- Reviewed, Sign Off Pending (pale blue) – The reviewer decided the record but has not signed off. These records remain editable, and the certification cannot act on them yet.
- Review Pending (grey) – No decision recorded against the record.
Hovering over the bar opens a breakdown with the exact counts behind each part: Total Records, Reviewed and Signed Off, Reviewed, Sign Off Pending, and Review Pending.
A certification showing a full pale blue bar means every assigned record carries a decision and none has been signed off. Reviewers in this position still have the Sign Off step to complete.
Steps to sign off:
-
Go to Access Reviews → Ongoing tab
-
Select the assigned certification
-
Select the assigned application or group
-
Complete review actions for all users
-
Confirm the top bar shows every assigned record as reviewed, for example 120 / 120 reviewed.
-
Select the Sign Off button at the top right
-
Select Confirm in the prompt.
Once signed off:
- All actions become locked and non-editable.
- The reviewer’s responsibility for the certification ends.
- The application moves to the next stage in the certification workflow.
Signing off acts as a final confirmation and is required before the certification can proceed to the remediation or completion phases.
9. Multi-Level Review Handling
Zluri supports multi-level reviews to accommodate scenarios where multiple validations of user access are required for compliance purposes. For detailed explanation, refer to How Sign-Offs and Multi-Level Reviews Work in Zluri
10. Reviewer Notification Triggers
Zluri keeps reviewers informed at key points to maintain timely completion and prevent bottlenecks.
-
Assignment of records
Zluri sends a notification immediately when new records are assigned to a reviewer.
-
Pending reviews (automatic reminders)
Zluri sends an automatic reminder 48 hours before the Review End Date to reviewers who still have pending records.
Zluri also sends an automatic reminder 48 hours before the Remediation End Date to the Certification Owner to close pending remediation tasks.
-
Pending reviews (manual reminders)
Certification Owners and Admins can send manual reminders at any time to selected reviewers who have pending actions or have not signed off.
-
Multi-level reviews
Zluri notifies the next-level reviewers as soon as the previous level signs off, indicating their level has started.
Delivery channels: in-app alerts and email by default; integrated messaging (e.g., Slack/Teams) if configured.
Updated about 4 hours ago